GitHub & GitLab support
Run STAR scans directly from your repo. Instant feedback and verified fixes appear where developers already work.
Bright STAR Harness
Bright STAR is an AI-powered AppSec platform that finds, fixes, and validates real vulnerabilities early in the SDLC — across both human and AI-generated code.
Book a demo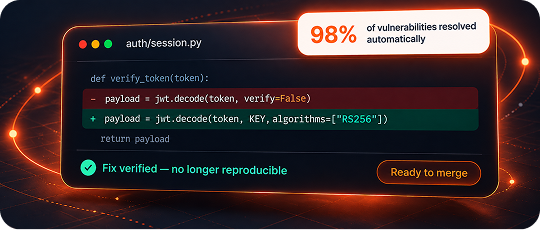
Trusted by security teams at companies like
The paradigm shift
Run STAR scans directly from your repo. Instant feedback and verified fixes appear where developers already work.
Automate scanning on every push, branch, or scheduled build. Shift left with confidence and keep visibility across the SDLC.
Business impact
Modern businesses can't afford security gaps that slow innovation or expose critical assets. Bright empowers teams to identify and remediate vulnerabilities early — without disrupting development velocity. By integrating security seamlessly into your pipeline, you reduce risk, accelerate releases, and protect what matters most: your customers, data, and brand reputation.
0%
of vulnerabilities are resolved automatically — cutting remediation time from weeks to minutes.
0%
Cut in remediation and fix-approval time
<0%
False positives, thanks to proof-based detection
0+
Validated security unit tests behind every fix
Security that moves your business forward
Bright STAR's AI-driven platform automatically detects, validates, and fixes vulnerabilities contributing to your security tech debt — combining auto-remediation, validation, and pull request automation to keep your codebase secure without manual firefighting.
98% resolved automatically
Bright STAR delivers developer-centric AppSec automation built to fit seamlessly inside GitHub, GitLab, and CI/CD pipelines — detecting vulnerabilities early and auto-remediating most issues before they ever reach production.
Cuts remediation time by 80%
Bright STAR integrates directly into your existing workflows, delivering real-time detection, auto-remediation, and compliance validation. It even works with AI coding tools like GitHub Copilot — scanning, testing, and fixing vulnerabilities before code ships.
AI compliance in 30 minutes
Bright STAR extends protection far beyond known endpoints, securing your entire API ecosystem — uncovering hidden APIs, mapping your complete attack surface, and validating every fix with live attack simulation.
Full OWASP API Top 10 coverage
How it works
As software development shifts toward AI-generated code, traditional security approaches fall behind. Bright STAR introduces a new model — continuous, autonomous security that validates real vulnerabilities in running applications.
Automatically scans your repositories to identify every code component, function, and dependency — detecting hidden or shadow APIs that traditional scanners often miss.
Uses advanced AI-based dynamic analysis to detect vulnerabilities in real time, observing live code execution to uncover flaws at the exact function or API endpoint.
Automatically proposes and validates fixes for detected vulnerabilities, iterating on each remediation until the issue is proven resolved through attack simulation — not assumption.
Automatically creates or updates pull requests populated with verified, AI-generated fixes, detailed vulnerability explanations, and relevant code references.
How Bright compares
Legacy tools rely primarily on static analysis, dependency scanning, and crawl-based testing — evaluating code patterns without executing the application. Bright STAR performs runtime, exploit-based dynamic testing, validating vulnerabilities in a live execution context.
| Operational outcome | Bright STAR | Legacy tools |
|---|---|---|
| False positives | <3% | Higher / moderate–high |
| Runtime validation | Yes | No |
| Logic flaw detection | Yes | Limited |
| CI/CD impact | Minimal | Moderate–high |
| Remediation confidence | Verified | Assumed |
| Developer workflow | PR-level automation | Manual triage required |
Book a demo
Tell us what you're facing in AppSec, and we'll scope the walkthrough to your stack.
Better security, faster delivery
Security testing
Security testing
Security testing
Bright STAR Harness is Bright's AI-powered AppSec platform. It finds, fixes, and validates real vulnerabilities early in the SDLC — across both human and AI-generated code — then proves each fix with live attack simulation.
Traditional DAST crawls and probes applications. Bright STAR adds runtime, exploit-based validation plus auto-remediation: it proposes a fix, re-tests the running app, and only then opens a pull request with a verified patch.
Yes for runtime validation. Bright STAR tests the live application so findings are proven exploitable, then re-tests after remediation to confirm the issue is no longer reproducible.
STAR Harness detects exploitable vulnerabilities including logic flaws, API and shadow-API issues, and OWASP API Top 10 risks — with proof-based detection that keeps false positives under 3%.
No. STAR Harness secures applications and APIs across the SDLC, including hidden or shadow APIs, and integrates with GitHub, GitLab, CI/CD, and AI coding tools such as GitHub Copilot.
Certifications and recognition