JUnit Testing: The Basics and a Quick Tutorial

Table of Content

  1. What Is JUnit Testing in Java Programming? 
  2. Importance of JUnit Testing 
  3. Core Features of JUnit 5
  4. Understanding Unit Testing Principles in Java
  5. Setting Up Your First JUnit Test Environment
  6. Common Assertions and Test Case Patterns in JUnit
  7. Integrating JUnit with CI/CD Pipelines
  8. Getting Started with JUnit Framework

What Is JUnit Testing in Java Programming? 

When you’re creating a Java application, you want to make sure it’s functioning as expected. This is where JUnit testing comes in. JUnit is a unit testing framework for the Java programming language. It plays a crucial role in test-driven development (TDD), where you write unit tests before writing the actual code. This ensures that your code is working correctly from the very beginning.

JUnit is an instance of the xUnit architecture for unit testing frameworks. It provides assertions to identify test methods, test-cases, setup methods, and so on. Note that JUnit is not built into the Java language, but it’s widely used by Java developers to perform unit testing.

Importance of JUnit Testing 

Ensuring Code Quality

JUnit plays a vital role in maintaining the quality of your code. Through JUnit testing, you can ensure that the logic of individual pieces of your software, known as units, are sound and working as expected. This can help you catch and correct bugs early in the development process, saving you time and ensuring a higher quality product.

Moreover, JUnit tests allow you to ensure that your code remains correct in the long run. As you change and refactor your code, you can run JUnit tests to make sure that you haven’t inadvertently introduced any new bugs. This makes maintaining your code easier and safer.

Learn more in our detailed guide to cypress testing.

Facilitating CI/CD

JUnit testing is also essential for facilitating continuous integration and continuous delivery (CI/CD). In a CI/CD pipeline, code is integrated, tested, and deployed frequently. JUnit tests can be automatically run every time code is integrated, ensuring that new changes don’t break the application.

Enhanced Collaboration

JUnit testing can also enhance collaboration within your development team. Since JUnit tests are code, they can be shared and updated by all members of your team. This means that everyone can contribute to maintaining the quality of the application, not just a dedicated testing team.

Furthermore, JUnit tests serve as a form of documentation. By reading the tests, developers can understand what a piece of code is supposed to do and how it’s expected to behave. This can make onboarding new team members easier and improve communication within the team.

Core Features of JUnit 5 

Annotations

JUnit 5 introduces a number of new annotations that simplify writing tests. For instance, @BeforeEach and @AfterEach annotations allow you to specify methods that should be run before and after each test. This can be useful for setting up or cleaning up resources that are used in your tests.

Assertions

Assertions are a key aspect of any testing framework, and JUnit 5 is no exception. Assertions let you verify that the application’s actual output matches the expected output. In JUnit 5, assertions are more powerful and flexible. For instance, you can use the assertAll method to group multiple assertions. If one assertion fails, the remaining ones will still be executed.

Test Runners

Test runners are another core feature of JUnit 5. A test runner is a tool that executes your tests and reports the results. In JUnit 5, the runner has been redesigned to be more flexible and powerful. For instance, you can use the @RunWith annotation to specify a custom runner.

Parameterized Tests

Parameterized tests are a powerful feature that allow you to run a test multiple times with different inputs. This can be especially useful when you want to test a method or function that should work with a range of input values. In JUnit 5, parameterized tests are easier to write and more flexible.

Exception Handling

In JUnit 5, exception handling has been improved. You can use the assertThrows method to assert that a specific exception is thrown. This makes testing methods that should throw exceptions easier and clearer.

Extensions

JUnit 5 introduces a new model that makes it easier to extend the framework. Extensions can be used to add behavior to tests, such as setting up resources, handling exceptions, or even altering how tests are executed. This makes JUnit 5 a more flexible and powerful testing framework.

Related content: Read our guide to mocha testing.

Understanding Unit Testing Principles in Java

When you are going through a Java JUnit tutorial, the first thing to understand is why Java unit testing matters in practice. Java unit testing is about testing pieces of Java code, usually individual Java methods, to make sure they behave as expected.

You do not have to wait until the whole Java application is built to test the Java code. Java developers test the Java logic early. This makes it easier to catch Java bugs before they spread. Good Java unit tests are simple, repeatable, and independent. They should not rely on Java systems like Java databases or Java APIs.

Java JUnit fits naturally into this Java approach. Java JUnit helps you write Java tests that check specific Java outcomes. Over time, these Java tests act like a safety net for your Java code. If something breaks after a Java code change, you will know immediately that the Java code change caused the problem.

Setting Up Your First JUnit Test Environment

When you are starting a Java JUnit tutorial, setting up the Java environment is usually easier than people expect. If you are using Java tools like Maven or Gradle, Java JUnit can be added as a dependency in a few lines of Java code.

Modern Java IDEs like IntelliJ IDEA or Eclipse already support Java JUnit out of the box. Once Java JUnit is added, you can create a Java test class that mirrors your Java class. The Java naming is usually straightforward, something like UserServiceTest for UserService.

Inside that Java class, you write Java methods annotated with @Test. That is all it takes to define a Java test. From there, you can run Java tests from the Java IDE and see Java results instantly. It is a Java setup, but it makes a big difference in how you write and verify your Java code.

Common Assertions and Test Case Patterns in JUnit

As you continue with a Java JUnit tutorial, you will start using Java assertions to verify Java behavior. Java assertions are basically Java checks. They compare expected Java results with Java output.

For example, Java assertEquals() checks if two Java values match, while Java assertTrue() verifies a Java condition. These are powerful Java assertions. Most Java tests rely on a few core Java assertions rather than anything complex.

There are also Java patterns that Java developers follow. One popular Java approach is Arrange-Act-Assert. First, you set up the Java data. Then you run the Java method. Finally, you check the Java result.

Keeping Java tests is important. If someone else looks at your Java test, they should quickly understand what it is verifying. Clean Java tests are just as important as Java code.

Integrating JUnit with CI/CD Pipelines

A Java JUnit tutorial does not stop at writing Java tests; it also shows how to run them automatically. This is where Java CI/CD comes in. Java tools like Jenkins, GitHub Actions, or GitLab CI can run your Java JUnit tests every time Java code is pushed.

The Java idea is simple. Before Java code gets merged or deployed, all Java tests must pass. If something fails, the Java pipeline stops. This prevents broken Java code from reaching Java production.

Over time, this builds confidence in your Java code. Java developers do not have to test everything; they rely on automated Java checks. It also encourages Java testing habits because failing Java tests are visible to the whole Java team.

Integrating Java JUnit into Java CI/CD is not complicated. It is one of the most valuable steps in modern Java development workflows.

Getting Started with JUnit Framework 

This tutorial will provide a step-by-step guide, complete with code examples, to help you get started with JUnit.

Step 1: Installing JUnit

The first thing you need to do is install JUnit. You can download JUnit as a .jar file from the official website, or you can use a build tool like Maven or Gradle to manage your dependencies. For Maven, you’ll need to include the following dependency in your project’s pom.xml file:


    junit
    junit
    4.12
    test

If you’re using Gradle, include this in your build.gradle file:

dependencies {
    testImplementation 'junit:junit:4.12'
}

Basic Structure of a JUnit Test

Once you’ve installed JUnit, it’s time to start writing your tests. At the most basic level, a JUnit test is a Java class with one or more test methods. Each test method is annotated with @Test and contains the code to test a particular unit of functionality. Here’s a simple example:

import org.junit.Test;
import static org.junit.Assert.assertEquals;
public class MyFirstJUnitTest {
   @Test
   public void testAddition() {
       int result = 1 + 1;
       assertEquals(2, result);
   }
}

In this example, the testAddition method tests whether the addition of 1 and 1 equals 2. If it does, the test passes. If it doesn’t, the test fails, and JUnit provides a helpful error message.

Running JUnit Tests

After writing your tests, you need to run them. You can run JUnit tests from the command line, from an IDE like Eclipse or IntelliJ IDEA, or from a build tool like Maven or Gradle. 

In this tutorial we’ll run the tests from the command line. Before proceeding, you will need to download junit-4.12.jar and hamcrest-core-1.3.jar.

To run the tests from the command line, compile your test class and then use the org.junit.runner.JUnitCore class to run the tests:

javac -cp .:junit-4.12.jar MyFirstJUnitTest.java
java -cp .:junit-4.12.jar:hamcrest-core-1.3.jar org.junit.runner.JUnitCore MyFirstJUnitTest

If you’re using an IDE, you can usually just right-click on the test class and select “Run As > JUnit Test.” For Maven, use the mvn test command, and for Gradle, use the gradle test command.

Making Assertions in JUnit

Assertions are the core component of your tests. They’re what allow you to verify that your code is working as expected. JUnit provides a variety of assertion methods, including assertEquals, assertTrue, assertFalse, assertNull, assertNotNull, and more. Here’s an example of how you might use assertions in your tests:

import org.junit.Test;
import static org.junit.Assert.*;
public class MySecondJUnitTest {
   @Test
   public void testStringConcatenation() {
       String result = "Hello" + " " + "World";
       assertEquals("Hello World", result);
       assertNotNull(result);
       assertTrue(result.length() > 0);
   }
}

In this example, the testStringConcatenation method tests whether the concatenation of “Hello”, ” “, and “World” equals “Hello World”. It also checks that the result is not null and that its length is greater than 0.

That’s all there is to creating a simple test case with JUnit. With practice, you’ll find that JUnit testing can be a vital part of your development process, helping to ensure that your code is robust, reliable, and ready for production.
JWT, or How I Left My Front Door Open

Table of Content

  1. JWT Basics
  2. Token Manipulation
  3. Everything but the kitchen sink

Imagine for a moment, the most exciting day for a product launch, main features developed, hearts palpitating, shoulders have been cried upon, many nights have been rushed working, product managers are exhausted, everybody is heavy, tears of joy rushing from their eyes…three, two, one and….Launch! 

The product is live as a SaaS service… A sigh has been communally shared, everything works, the customers can login, they see the shiny menu that your new UX designer has worked so hard to create.  A day passes, two, a week…and then something weird happens: Some customers complain that the data displayed on their dashboard is incorrect, some users have been added to their organization or some data is missing, but what could be the culprit?


In the case that the product uses JWT (JSON Web Tokens) for authentication, there could potentially be multiple issues if not implemented correctly. In this article we will try to address JWT and its implementation in the following sections.

JWT Basics

JSON Web Tokens (Shortened JWT) are a method of transferring small structured parts of information between parties in a trusted or secured manner. Trusted meaning signed by a verified public key versus Secured meaning encrypted by a known secret key.

These JWT tokens are most commonly used as either authorization mechanisms or encryption methods, we will focus on the authorization part in this document as this is the scenario that is most interesting to us (and is actually the most prevalent).

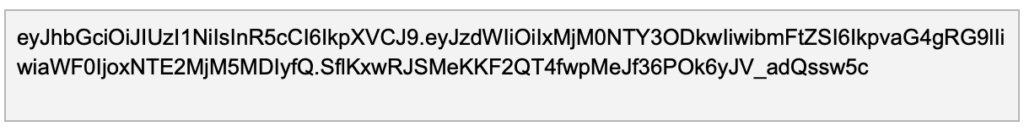
Let’s assume for the sake of our discussion that we have Jimmy, he is a user of our SaaS application; Jimmy starts his day by logging in to the application, his credentials are being verified by either a local users repository or a third party provider, the authentication succeeded and now Jimmy receives a JWT Token which looks like this:

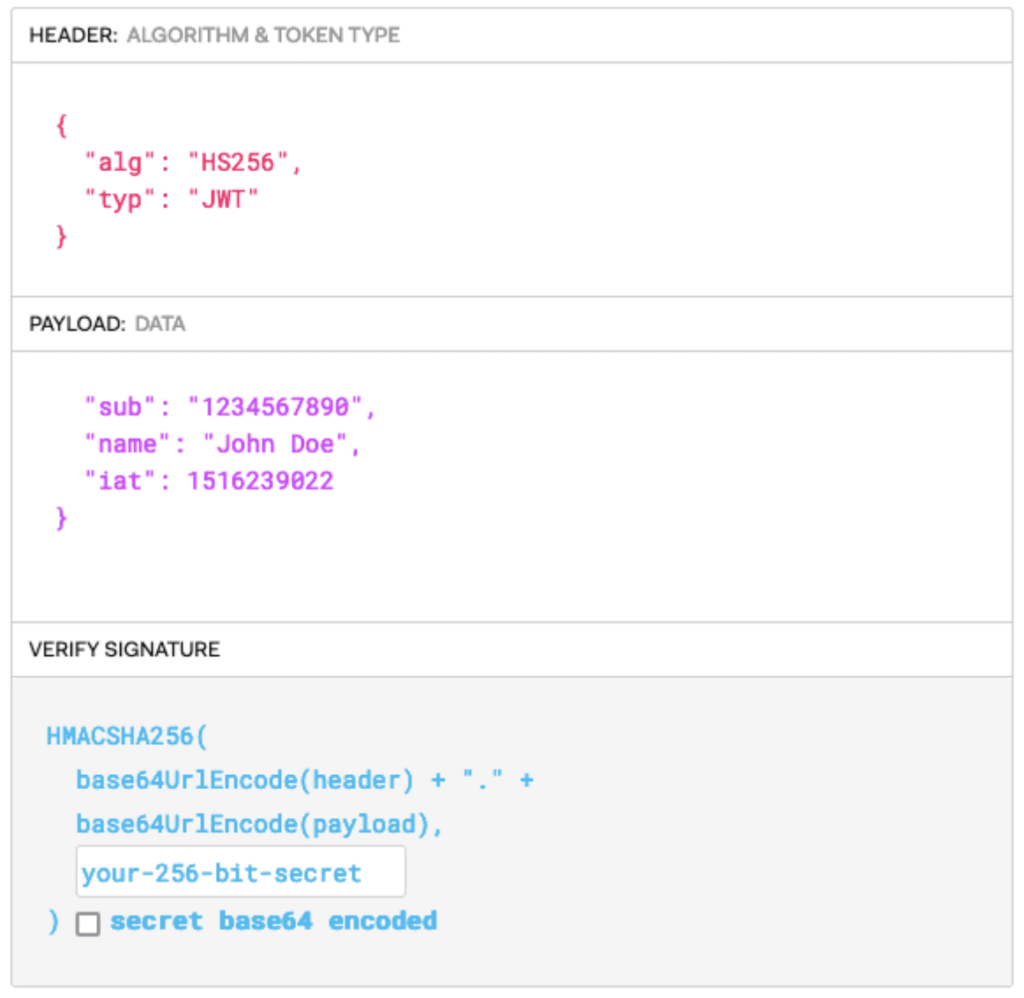
Looks fun doesn’t it? Oh, wait, it’s encoded, let’s break it down for a second, in decoded form it looks like this:

The token is split into three parts: 

  • The header: defines what type of token it is and what algorithm is used to sign the validity of the token
  • The payload: which will contain information about who the token was signed for, the role or the authorization of the user, the identity of the user, the timestamp of the token, etc.
  • The verify signature part: this will include the signature of the token, and the secret if needed.

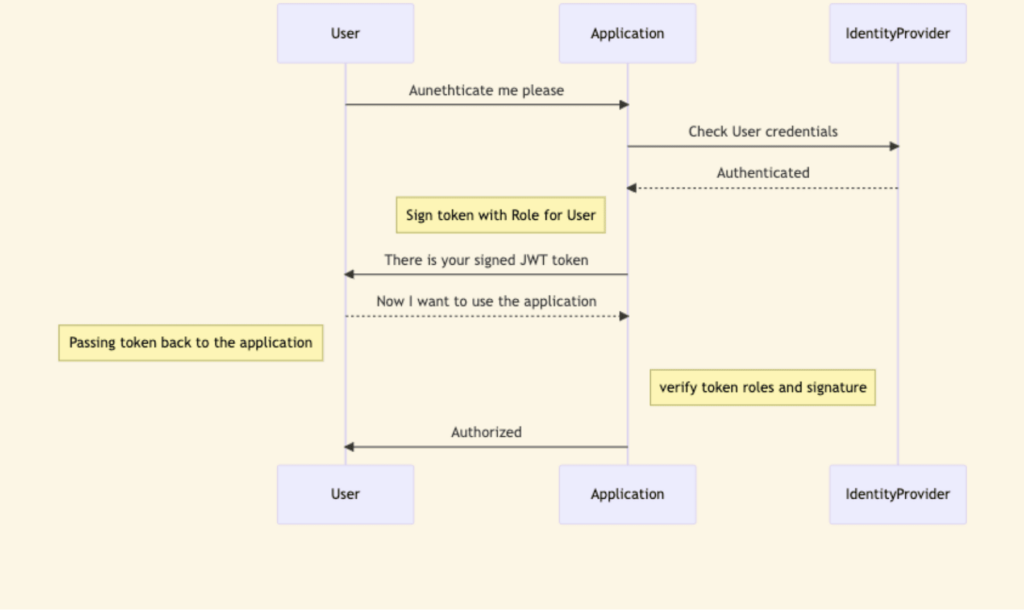
This token is passed from the application to the user and is usually submitted back in the Authorization header, this way the application verifies the authenticity of the token and checks the user role / identity that will have access to the application.

The server signs the token with its own key, that way it can verify that the contents are not modified and that the token was indeed issued by the server.

The application flow will look something like this:

Token Manipulation

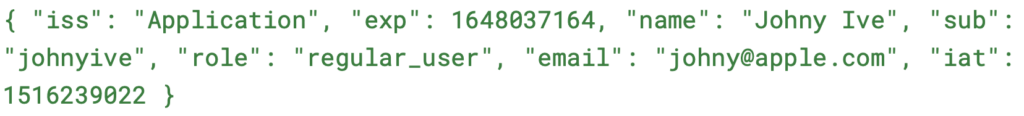
Now that we know what the regular mechanism of JWT looks like, let’s try to see what can (and a lot of times can) go wrong, there are multiple ways to attack the application that uses JWT tokens, let’s assume that our token looks like this (after the decoding that is):


The attacker will want to access the application, maybe change the permissions or impersonate a different user, our only method of checking the validity of the token is the strength and the security of the signing key. For example if the attacker will modify the Role field to Admin in the application and the application doesn’t re-check the role, the user can access Administrative functions, as long as the signature is valid, at least we can be sure that the token is valid and was not manipulated before sending back to the application.

Some attack vectors in this scenario will try to address the header first:

  • Modifying or downgrading the Algorithm of the token: setting the Alg field to none, if the application allows it, will mean that there is no signature, thus allowing the attacker to change every field of the token and impersonate anyone, attacker can also try to downgrade the algorithm to a weak algorithm will allow the attacker to Brute force the key to the token and sign his own tokens instead.

Modifying header parameters: changing fields like JWK, JKU or KID, allow the attacker to either refer to a different signing key that will be used for token verification or to a blank key, for example can use his own key to sign the token and embed it into the JWK header or refer the server to the URL of the key used to sign using the JKU and submit self signed tokens to the application.

Everything but the kitchen sink

If an attacker can create or sign false tokens to the application, this effectively means that the authorization mechanism is basically broken, he can impersonate any user or role within the application thus gaining access and performing any damage that he wants with the impersonated user’s identity.

So, what can be done about it? Let’s put it into the Do’s and Don’ts of using JWT tokens:

Do:

  • Rotate signing keys periodically, so that if the key is exposed the tokens that are signed will be exposed for a short time, minimizing the threat.
  • Secure your keys, don’t store them in the application, better to store them in a cloud KeyVault / KMS.
  • Verify the role signed in the token vs the user repo.
  • Verify the Signing key and URL, don’t allow URLs from locations that you don’t control in the JKU
  • Set the token expiration to the shortest time required, don’t issue tokens that have long expiration times

Don’t:

  • Trust external JKU locations
  • Allow KID (Key Identifiers) to be set for inexistent keys
  • Try to write your own frameworks to decrypt keys
  • Try to use homegrown Encryption algorithms
  • Use weak keys or allow to downgrade the Hashing algorithms

Unit Testing vs. Integration Testing: 4 Key Differences and How to Choose

Table of Content

  1. What Is Unit Testing? 
  2. What Is Integration Testing? 
  3. Unit Testing vs. Integration Testing: Key Differences 
  4. Unit Testing and Integration Testing: When to Use 

What Is Unit Testing? 

Unit testing is a software testing technique where the individual components or units of a product are tested. Its purpose is to confirm whether each unit of the code performs as expected. Essentially, the “unit” in Unit Testing refers to the smallest testable part of an application. This could be a function, a procedure, an interface, or a method, depending on the specific programming language you’re working with.

In unit testing, each section of code is isolated and tested separately to ascertain its correctness. This isolation is vital for accurate results, as it ensures that the test is focused solely on the unit in question, without any interference from other parts of the code. Unit testing is usually conducted by the developers themselves, immediately after a specific function or method has been developed.

Unit testing is a fundamental part of the software development process. It helps in identifying and fixing bugs at an early stage, making the code more reliable and robust. When changes are made to the software, previously written unit tests can provide assurance that the existing functionality still works as intended.

What Is Integration Testing? 

Integration testing is a software testing approach in which individual software modules are combined and tested as a group. The primary purpose of integration testing is to expose flaws in the interactions between integrated units.

In contrast to unit testing, where individual units are isolated and tested separately, integration testing focuses on the interfaces and interaction between units. It aims to detect issues that may arise when different components interact with each other, such as data inconsistencies, communication problems, or function mismatches.

Integration testing is generally performed after unit testing and before system testing in the software testing process. It is typically carried out by a testing team, rather than the developers themselves. While this type of testing can be more complex and time-consuming than unit testing, it is crucial for ensuring that all parts of the system work together correctly.

The following diagram illustrates the position of unit tests and integration tests in the overall ‘testing pyramid’. Unit tests are at the base of the pyramid, indicating that typically, there will be more unit tests than any other testing type.

In this article:

Unit Testing vs. Integration Testing: Key Differences 

Understanding the differences between unit testing and integration testing is vital for applying the right testing strategy at the right time. These differences can be categorized in the following ways:

1. Component-Level vs Interaction-Level

The fundamental difference between unit testing and integration testing lies in the level at which testing is performed. Unit testing is a component-level testing method. It focuses on testing individual components or units of a software in isolation. On the other hand, integration testing is an interaction-level testing method. It focuses on testing the interaction between different components of a software.

2. Complexity

Unit testing is simpler and more straightforward than integration testing. Since unit testing involves testing individual components in isolation, it’s easier to pinpoint the cause of a failure. Conversely, integration testing, which tests the interaction between different components, is more complex because a failure can be due to a multitude of factors.

3. Speed and Efficiency

Unit testing is usually faster and more efficient than integration testing. This is because it’s easier and quicker to test a single component in isolation rather than multiple components together. However, while unit testing can help catch issues early, it cannot identify problems that may arise when different components interact. This is where integration testing comes in, providing a more comprehensive check of the system’s functionality.

4. Tools and Technologies

For unit testing, tools like JUnit, NUnit, and PHPUnit are typically used. These tools provide a framework for writing and running test cases and are usually integrated with the development environment. For integration testing, tools like Jenkins, Bamboo, and TeamCity are often used. These tools help in automating the process of combining and testing different components together.

Learn more in our detailed guide to unit testing best practices 

Unit Testing and Integration Testing: When to Use 

Unit Testing

Early Development Stages

During the early stages of development, when individual software components are being written, unit testing proves to be invaluable. It helps developers to identify and rectify any issues in their code at an early stage, thus saving time and effort in the long run. By testing each unit in isolation, developers can ensure that their code behaves as expected under different scenarios.

Continuous Development

In the realm of Continuous Integration and Continuous Delivery (CI/CD), where new code is constantly being integrated and deployed, unit testing plays a critical role. It provides a safety net that allows developers to add new features or make changes to the existing codebase confidently. If the new code causes any existing unit tests to fail, developers can quickly identify and rectify the issue before it affects the rest of the application.

Refactoring

When it comes to refactoring, or altering the code to improve its structure without changing its behavior, unit testing is a developer’s best friend. A comprehensive set of unit tests can serve as a reliable indicator that the refactoring process has not inadvertently altered the functionality of the code. This facilitates a smooth and efficient refactoring process, ensuring the integrity of the codebase.

Isolated Functionality Testing

Unit testing is also useful when it comes to testing isolated functionality. Unit tests allow developers to verify the functionality of each component in isolation, without having to test the rest of the application. This helps ensure that each component behaves as expected, regardless of the state or behavior of other components.

Learn more in our detailed guide to unit testing vs functional testing 

Integration Testing

After Unit Testing

Once all the individual components of the software have undergone unit tests, it’s time to move on to integration testing. This type of testing ensures that the different components of the software work together as expected. It helps to identify any issues that may arise due to the interaction of different components, which might not have been evident during unit testing.

Complex Systems with Multiple Interactions

In complex systems where multiple components interact with each other, integration testing allows developers to verify that the interactions between different components are functioning as expected. This is particularly important in today’s world of microservices and distributed systems, where a single application may consist of numerous interconnected components.

Validating Data Flow

Integration testing also plays a key role in validating data flow between different components of a software. It verifies that data is correctly passed between different components and that no data is lost or incorrectly altered in the process. This is particularly important in applications where accurate data handling is critical, such as financial or healthcare applications.

End-to-End Testing Scenarios

Integration testing ensures that the entire application, from the front-end user interface to the back-end database, works as expected under different scenarios. It helps to identify any issues that may arise when the application is used in a real-world scenario.

Learn more about Bright Security

Best Practices for Secure Coding in Web Applications

Table of Content

  1. Input Validation and Sanitization 
  2. Authentication and Authorization 
  3. Secure Data Storage and Transmission
  4. The Principle of Least Privilege 
  5. Regular Security Updates and Patching
  6. Embracing Secure Coding 

Secure coding refers to the practice of writing software code in a manner that minimizes vulnerabilities and guards against potential cyber threats. It involves adhering to established coding standards, employing robust coding techniques, and leveraging security best practices throughout the software development lifecycle. Secure coding serves as a primary defense against malicious attacks and vulnerabilities that could otherwise compromise the confidentiality, integrity, and availability of software systems. 

Insecure code, on the other hand, exposes web applications to a multitude of risks, ranging from injection attacks, cross-site scripting, and data breaches, to denial-of-service exploits and unauthorized access. Such vulnerabilities can lead to severe consequences, including the unauthorized disclosure of sensitive information, disruption of services, and damage to an organization’s reputation. Therefore, embracing secure coding practices is not only a technical necessity but also a fundamental step towards building resilient and trustworthy web applications.  


In this blog post we will explore five essential secure coding best practices:

  1. Input Validation and Sanitization
  2. Authentication and Authorization
  3. Secure Data Storage and Transmission 
  4. The Principle of Least Privilege 
  5. Regular Security Updates and Patching

Input Validation and Sanitization 

Perhaps the most important practice is input validation which is the process of examining data that is entered into a software application to verify  that it conforms to specified formats and criteria. For example, input validation would expect integers between 1 and 12 for the correct input for a month value. The goal of input validation is to prevent potentially malicious data from causing issues within the application. By validating inputs, developers can ensure that only data meeting predefined standards is accepted, reducing the risk of security vulnerabilities. 

Input sanitization, on the other hand, involves cleaning or filtering input data to remove any characters, symbols, or elements that could potentially be exploited by attackers to inject malicious code or disrupt the applications behavior. An example of unusual characters includes quotation marks inside of a text field which may be indicative of an attack. Sanitization ensures that even if validation fails and potentially harmful data gets through, it is neutralized before being processed, displayed, or stored. 

Both input validation and sanitization are vital for making web applications secure. Making sure that user inputs are trustworthy is crucial to stopping various online dangers. By carefully checking data against known standards and thoroughly cleaning it to remove any harmful parts, developers can stop vulnerabilities like SQL injection and cross-site scripting attacks. This method acts as a strong shield, making web applications strong against unauthorized access and keeping user information safe. 

Authentication and Authorization 

Authentication is the process of verifying the identity of a user, system, or entity attempting to access a particular resource or system. It ensures that the individual or entity is who they claim to be. In the context of web applications, authentication involves validating user credentials, such as usernames and passwords, and sometimes additional factors like security tokens or biometric data. Authentication prevents unauthorized individuals from gaining access to sensitive information or functionalities. 

In contrast, authorization determines what actions an authenticated user is allowed to perform within the system. It specifies the permissions and privileges associated with a user’s identity. Authorization ensures that authenticated users only have access to the resources, features, and data that they are entitled to use. This prevents users from overstepping their boundaries and helps protect sensitive information from being accessed or manipulated by unauthorized parties. 

In essence, authentication confirms who you are, while authorization defines what you are allowed to do once your identity is confirmed. Both authentication and authorization are crucial components of web application security, working together to ensure that only legitimate users can access appropriate resources and perform authorized actions. 

Secure Data Storage and Transmission

Secure data storage refers to the practice of safeguarding sensitive information, such as user credentials, personal data, and confidential documents, in a way that prevents unauthorized access, tampering or theft. This involves using encryption, access controls, and other techniques to ensure that data is stored in a protected manner. 

Secure data transmission involves ensuring that data transferred between users and the web application or between different components of the application is encrypted and cannot be intercepted or manipulated by malicious actors during transit. This is typically achieved using protocols like HTTPS, which encrypts data exchanged between a user’s browser and web server. 

Secure data storage and transmission are integral to the over security posture of web applications. Implementing robust encryption, access controls, and following best practices for data handling contribute significance to a web application’s ability to protect user data and maintain its integrity. 

The Principle of Least Privilege 

The Principle of Least Privilege is a fundamental security concept that mandates  that any user, process, or entity should be granted the minimum necessary access rights, permissions, and privileges required to perform their tasks and nothing more. Applying this principle aims to reduce the potential impact of security breaches. By limiting the scope of access, the attack surface available to potential threats is minimized, making it more difficult for attackers to exploit vulnerabilities or gain unauthorized access to critical systems, data, or resources. 

In the context of web applications, following the Principle of Least Privilege involves designing and implementing role-based access controls, employing proper authentication and authorization mechanisms, and continuously reviewing and adjusting permissions as needed. While it may require additional effort to carefully define and manage access levels, the benefits far outweigh the potential risks associated with granting excessive privileges. 

Regular Security Updates and Patching

Regular security updates and patching involves consistently updating software components, libraries, frameworks, and the underlying infrastructure to address known vulnerabilities and security weaknesses. This practice is crucial for maintaining the security and integrity of web applications over time. 

Incorporating regular security updates and patching into the development process is a proactive approach that demonstrates a commitment to security and helps protect web applications from evolving cyber threats. 

Embracing Secure Coding 

In today’s digital landscape, secure coding in web applications is not just a choice but a necessity. The principles discussed above form a robust framework for building and maintaining secure web applications. Implementing input validations, authentication and authorization, secure data handling, the principle of least privilege, and regular updates enhances application security. These practices collectively counter cyber threats, safeguard data, and build user trust. By combining thoughtful practices and ongoing improvement, web applications can confidently navigate the digital realm, upholding privacy and reliability. 

How I Bypassed an Imperva WAF and Obtained XSS

Table of Content

  1. Summary:
  2. Bypassing an Imperva WAF and obtaining XSS
  3. Conclusion

Summary:

Cross-Site Scripting (XSS) is a type of security vulnerability commonly found in web applications. It occurs when a web application allows malicious actors to inject malicious code (usually JavaScript) into web pages viewed by other users. This allows the attacker to execute arbitrary code within the context of another user’s browser, potentially stealing sensitive information, manipulating content, or performing actions on behalf of the victim user.

XSS vulnerabilities can be classified into three main types:

1. Stored XSS (Persistent XSS):

In this type of XSS, the malicious code is permanently stored on the web server, often in a database. When a user requests the compromised page, the server includes the malicious code in the response, which then gets executed by the victim’s browser. This is particularly dangerous as the malicious code affects every user who accesses the compromised page.

2. Reflected XSS:

Reflected XSS involves injecting malicious code into a web application’s input (such as a search bar), and then the application reflects that code back to the user as part of the response. The attacker often tricks the victim into clicking a malicious link that contains the injected code. Once the victim clicks the link, the malicious code executes in their browser. Unlike stored XSS, this attack is not persistent and only impacts users who interact with the malicious link.

3. DOM-based XSS:

DOM-based XSS exploits vulnerabilities in the Document Object Model (DOM) of a web page. Instead of modifying the actual page content on the server, the attacker manipulates the DOM elements using JavaScript to execute malicious code in the victim’s browser. This type of XSS doesn’t rely on server responses to deliver the payload, making it harder to detect.

Mitigating XSS vulnerabilities involves several security practices:

1. Input Validation and Sanitization:

Web applications should validate and sanitize user inputs to prevent any malicious code from being executed. Input validation involves checking that user inputs match expected formats, while input sanitization involves removing or encoding potentially dangerous characters.

2. Output Encoding:

All user-generated content that’s displayed on a web page should be properly encoded before being rendered. This prevents browsers from interpreting malicious code as executable content.

3. Content Security Policy (CSP):

CSP is an HTTP header that helps mitigate XSS attacks by specifying which sources of content are considered safe to load on a web page. This can prevent inline scripts and restrict the loading of external scripts to trusted domains.

4. Escape User Inputs:

Escape characters that might be interpreted as code when rendering user-generated content. This ensures that even if malicious code is injected, it’s treated as plain text and not executed.

5. Regular Security Audits:

Regularly audit and scan web applications for vulnerabilities, including XSS. Automated tools and manual code reviews can help identify and remediate potential issues.

Bypassing an Imperva WAF and obtaining XSS

Bug bounty programs and bug hunting are gaining more popularity each year. One of the old and popular vulnerabilities is XSS, specifically reflected XSS. Finding a reflected XSS is quite easy and doesn’t require significant effort to prepare the right payload and trigger a simple alert box if the server doesn’t filter user input. To prevent reflected XSS, developers use various forms of protection, whether it’s input sanitization or using a different WAF (Web Application Firewalls).

Today, we’ll discuss a technique to bypass an Imperva WAF. I will describe in detail how I managed to bypass Imperva’s protection and obtain a reflected XSS on a private bug bounty program.

Note: I will not disclose the actual domain where this type of XSS was found. Instead, throughout this article, I will refer to this domain as redacted.com.

Typically, before commencing web testing, bug hunters engage in information gathering and attempt to understand the functionality of the website. This is exactly what I started doing. The website itself returned the following response:

Reference #30.9f861402.1691918727.ef5e929

I found this response intriguing, and I began brute-forcing directories and files. After some time, I discovered a registration form on the website:

https://REDACTED.COM/REDACTED/account/registration/registration.jsp?redirectURL=/REDACTED/cart/cart.jsp

After a series of manipulations with this endpoint, it became evident that the values of the redirectURL parameter were reflected in the response. This led me to the idea of testing for reflected XSS.

Usually, when testing for reflected XSS, the goal is to identify where in the response the reflection occurs. It turned out that the reflection was happening within an HTML input tag, specifically in the value attribute:

To confirm this, I sent a simple string xssHere to recheck the reflection. In the response, I received the following:

Since the reflection was occurring within the input tag’s attribute, I needed to break out of the attribute and add an event handler with an alert to trigger a popup without user interaction. The payload used was ” autofocus /onfocus=”alert(1)

But Imperva blocked this request. The next idea was to break out of both the attribute and the tag and introduce a new HTML element with an alert box, which also resulted in the request being blocked. Following this, I attempted to identify any HTML elements that were blocked through fuzzing, but unfortunately, all elements were being blocked by the WAF. The characters < and > were not blocked or filtered by the firewall, but requests like were blocked.

To overcome this limitation, I tried URL-encoding characters after the < symbol, which initially didn't work. However, this didn't discourage me. I needed to think outside the box, and the idea of sending a request with invalid URL encoding came to mind.

After several manipulations, it turned out that if I sent an incorrect URL encoding, some characters were being converted. For instance, %5K was being converted to the symbol `P`, which opened up the possibility of crafting a new XSS payload.

I assembled the following payload:

%3C%5K/onpointerenter=alert(1)>

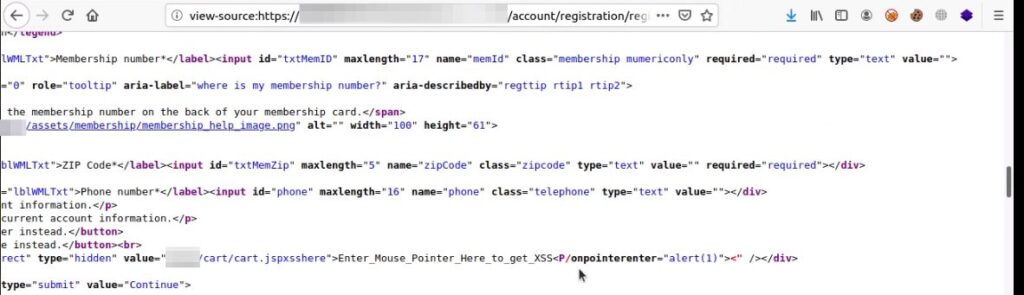
This payload, in the response, became:

The final payload was:

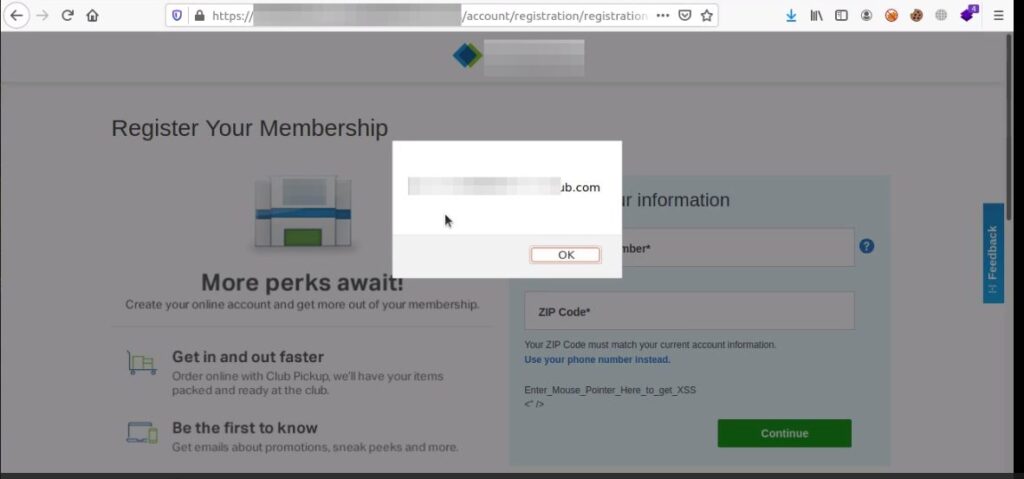
%22%3EEnter_Mouse_Pointer_Here_to_get_XSS%3C%5K/onpointerenter=alert(location)%3E%3!–

Upon hovering the mouse pointer over the text Enter_Mouse_Pointer_Here_to_get_XSS, I successfully triggered the working XSS.

Conclusion

A Web Application Firewall (WAF) can be an effective tool in mitigating Cross-Site Scripting (XSS) attacks, but it should not be relied upon as the sole line of defense. However, WAFs may not catch every possible XSS attack, especially if an attacker uses a new or highly obfuscated technique. Some attackers may find ways to bypass the rules of a WAF, leading to potential vulnerabilities. While a WAF can be a valuable component in your security posture against XSS attacks, it should be used in conjunction with other security best practices. Adopting a comprehensive approach that includes secure coding practices, regular security testing, and user awareness training will offer a more robust defense against XSS and other web application threats.

Why Input Validation Matters for Application Security

Table of Content

  1. Understanding Input Validation 
  2. Benefits of Proper Input Validation 
  3. Common Input Validation Techniques 
  4. Implementing Effective Input Validation 
  5. Empowering Digital Security Through Input Validation 

In today’s rapidly evolving digital landscape, where technology fuels both innovation and convenience, ensuring the security of our digital assets remains a critical concern. At the heart of creating robust application security lies the fundamental and most important concept of input validation.  In this blog post, we will introduce the significance of input validation and its impact on fortifying our digital defenses against a range of potential attacks. 

Understanding Input Validation 

Input validation refers to the process of scrutinizing and filtering data entered into a system, ensuring its adherence to predefined rules and constraints. Consider it as an inspector for the information we put into computer programs or websites. Its main job is to make sure that the things we type or send to these systems are safe and won’t cause any problems. Just like how we double-check our work before submitting it, input validation checks that the information we provide follows the rules and won’t harm the system. Its purpose is to prevent mistakes or malicious actors from getting inside and causing harm. 

When we don’t properly check the information we give to computer programs or websites, it can lead to trouble. Unvalidated inputs, which are like unchecked data, can create problems. For example, they might make the program show or do things it shouldn’t, or even let attackers  into the system. This can result in unauthorized access, where someone can see things they’re not supposed to, or it can lead to sensitive information being exfiltrated. Common security attacks that take advantage of this situation include injecting harmful code into the system or making it show fake information. These kinds of attacks can tamper with the program or steal important data, which is why it is crucial to properly validate inputs to keep your organization safe.

Benefits of Proper Input Validation 

Implementing strong input validation mechanisms offers a range of benefits that contribute to the overall security and reliability of computer programs and websites. One of the key advantages is improved security, as proper validation helps prevent unauthorized access, information disclosure and potential data breaches. Input validation is a crucial security measure to prevent a variety of common injection attacks, such as SQL Injection, Command Injection, and Cross-Site Scripting (XSS).

Input validation verifies that values provided by a user match a programmer’s expectations before allowing any further processing. By thoroughly checking the information entering the system, it becomes much harder for unwanted attackers to sneak in. Furthermore, input validation serves as a protective shield against various types of security attacks. It acts as a barrier and the first line of defense, preventing harmful code or malicious data from causing harm. This not only safeguards the system but also the data within it. 

Input validation also plays a crucial role in maintaining the accuracy and integrity of data. By ensuring that only valid and trustworthy information is accepted, it prevents errors or inconsistencies that could compromise the quality of data stored or processed. For example, proper input validation would check if a month entered fell between 1 and 12. Without proper validation, erroneous data could be entered or crash the application.  In essence, strong input validation is a frontline defense, fortifying applications against unauthorized access, attacks, and maintaining the reliability of the information they handle. 

Common Input Validation Techniques 

Client-Side Validation 

Client-side validation is like a friendly helper right at your fingertips when using computer programs or websites. It’s the immediate check that happens on your own device as you type information. This quick validation helps catch simple mistakes or missing details before you even submit anything. For example, If you forget to put your email address in the right format, client-side validation would give you an error message  right away. While it’s helpful for giving instant feedback and making sure you’re on the right track, it’s important to remember that it’s not the only line of defense. Stronger security measures and defense in depth are needed to ensure that everything is safe and secure on a bigger scale. 

Server-Side Validation  

Server-side validation is like a watchful guardian that stands behind the scenes when you interact with computer programs or websites. Unlike client-side validation, which happens on your device, server-side validation takes place on the actual server where the program or website is hosted. It’s an extra layer of security that ensures the information you provide meets all the necessary rules and standards, even if someone tries to bypass the client-side checks. This thorough validation helps prevent any incorrect or harmful data from entering the system, making sure that the program works as intended and that your data remains safe. Server-side validation is like the last checkpoint before any data gets processed, acting as the final safeguard against potential security risks and errors. 

Regular Expressions

Regular expressions, often called regex, are like magic patterns for searching and matching text within computer programs or websites. They’re powerful search queries that can find specific words, numbers, or patterns in a sea of information. Using a combination of characters and symbols, regular expressions allow you to define complex criteria for identifying and manipulating strings of text. Whether it’s validating email addresses, checking for phone numbers, or searching for specific keywords, regular expressions provide a versatile tool to handle a wide range of text-related tasks. While they might seem a bit cryptic at first, mastering regular expressions can unlock a whole new level of control and precision in managing and processing data. 

Whitelisting and Blacklisting 

Whitelisting and blacklisting, also now commonly referred to as “allow list” and “deny list”,  are two different approaches to managing access and permissions within computer programs or websites. Whitelisting is the most effective form of input validation and is like having a VIP list, where only the explicitly approved items or entities are allowed, and everything else is denied. It’s a strict and cautious method that ensures only trusted elements can interact with the system. On the other hand, blacklisting works like a list of things to avoid, where specific items are identified as problematic and blocked, while everything else is permitted. While both approaches have their merits, whitelisting is often considered more secure as it only permits known and verified entities, reducing the chances of unforeseen vulnerabilities. Blacklisting, while useful, can sometimes miss new or creative ways that attackers might try to breach the system. The choice between these two methods depends on the level of control and security required for a particular system or application. 

Implementing Effective Input Validation 

Implementing effective input validation is crucial to building secure and reliable computer programs or websites and considered the go-to standard for protecting against injection attacks. Best practices for input validation involves a combination of strategies aimed at ensuring that the data entering the system is safe and accurate. Firstly, adopt a comprehensive approach by validating inputs both on the client-side and server-side. Client-side validation provides quick feedback to users, while server-side validation acts as the final line of defense. Secondly, use strong validation techniques like regular expressions to define precise patterns that valid inputs must match. This prevents both common and complex input errors from sneaking through such as special characters often used in attacks. Thirdly, employ whitelisting and blacklisting techniques, reducing the risk of unexpected data causing issues. Regularly update validation rules to adapt to changing requirements and potential vulnerabilities. By consistently staying informed about the latest security trends and techniques, you can stay ahead of potential threats. In essence, combining various methods and keeping validation practices up-to-date is the key to fortifying your system against potential security vulnerabilities. 

Empowering Digital Security Through Input Validation 

In the dynamic digital world, where innovation and convenience are powered by technology, securing our digital assets stands as an essential concern. Throughout this blog post, we’ve introduced the significance of input validation and its robust impact on preventing security vulnerabilities. By adopting best practices and diligently implementing thorough validation techniques, organizations become empowered to withstand a broad spectrum of potential threats. As we navigate the line between innovation and security, input validation remains a powerful tool, if not the most important for enabling us to shape a digital landscape that can withstand evolving security challenges.

How DAST Supports PCI DSS Compliance

Table of Content

  1. PCI DSS details 
  2. Where does DAST fit in? 

By mapping Dynamic Application Security Testing (DAST) to the Payment Card Industry Data Security Standard (PCI DSS) requirements, organizations can effectively strengthen their application security and ensure compliance with industry standards. DAST provides a proactive approach to security by enabling businesses to identify vulnerabilities and address them before they can be exploited, thus safeguarding cardholder data and minimizing the risk of data breaches.

Integrating DAST into the PCI DSS security framework allows organizations to adopt best practices in vulnerability management and risk mitigation. By regularly scanning and testing web applications, businesses can identify and remediate security flaws, ensuring the ongoing protection of sensitive payment card information. This proactive stance not only strengthens the overall security posture but also directly demonstrates a commitment to compliance and the protection of customer data.

Moreover, incorporating DAST as a standard practice in the Secure Development Lifecycle (SDLC) ensures that security is ingrained throughout the application development process. By detecting vulnerabilities early on, organizations can address them during the development and testing stages, reducing the potential for security issues in the final product. This approach improves the overall security of applications and reduces the need for costly remediation efforts later on.

By integrating DAST into their security practices, organizations enhance their overall security posture, maintain compliance with PCI DSS, and build trust with customers. This approach ensures the effective protection of cardholder data and minimizes the risk of data breaches, contributing to a secure and reliable payment card environment.

PCI DSS details 

PCI DSS is a set of security standards designed to protect cardholder data and ensure the secure handling, storage, and transmission of payment card information by organizations that accept, process, or store such data. 

PCI DSS consists of 12 high-level requirements that organizations must meet to ensure the security of cardholder data. These requirements are as follows:

1. Install and maintain a firewall configuration to protect cardholder data.
2. Do not use vendor-supplied default passwords or security parameters.
3. Protect stored cardholder data.
4. Encrypt transmission of cardholder data across open, public networks.
5. Use and regularly update antivirus software or programs.
6. Develop and maintain secure systems and applications.
7. Restrict access to cardholder data by business need-to-know.
8. Assign a unique ID to each person with computer access.
9. Restrict physical access to cardholder data.
10. Track and monitor all access to network resources and cardholder data.
11. Regularly test security systems and processes.
12. Maintain a policy that addresses information security for all personnel.

These requirements provide a framework for organizations to protect sensitive cardholder data and maintain a secure environment for handling payment card transactions.

PCI DSS is not a regulation in the traditional sense; rather, it is a set of security standards established by the Payment Card Industry Security Standards Council (PCI SSC). These standards are designed to ensure the protection of cardholder data and reduce the risk of data breaches within the payment card industry. 

Compliance with PCI DSS is mandated by card brands and enforced by payment card acquirers and processors, making it a crucial requirement for organizations that handle payment card information. By adhering to PCI DSS, businesses demonstrate their commitment to maintaining a secure environment for processing, storing, and transmitting cardholder data.

Where does DAST fit in? 

DAST aligns to the 6th PCI DSS requirement; developing and maintaining secure applications. In PCI-speak this means to maintain a Vulnerability Management Program. PCI defines vulnerability management as the process of systematically and continuously finding weaknesses in an entity’s payment card infrastructure system. 

Specific to DAST,  PCI DSS Requirements 6.1 and 6.3 states that information security be incorporated into the SDLC. 

6.1 Establish a process to identify security vulnerabilities, using reputable outside sources, and assign a risk ranking (e.g. “high,” “medium,” or “low”) to newly discovered security vulnerabilities.
6.3 Develop internal and external software applications (including web-based administrative access to applications) securely, as follows: In accordance with PCI DSS (for example, secure authentication and logging)Based on industry standards and/or best practices Incorporating information security throughout the software-development life cycle

By using DAST, organizations shift application security left by test early, often and throughout the SDLC. DAST can help developers during unit testing  and throughout the SDLC by identifying vulnerabilities and security weaknesses in the application’s code. 

DAST scans the application in its running state, simulating real-world attacks, and provides immediate feedback to developers, enabling them to address security issues early in the development cycle and improve the overall security of the application. 

Here’s how DAST can assist with PCI DSS compliance:

Vulnerability Detection: DAST tools scan web applications for common security vulnerabilities such as cross-site scripting (XSS), SQL injection and insecure session management. By identifying these vulnerabilities, organizations can remediate them before they can be exploited by attackers and potentially compromise cardholder data.

Continuous Monitoring: PCI DSS requires regular vulnerability assessments and security testing. DAST tools can be employed to perform ongoing scans and tests in the CI/CD ensuring that vulnerabilities are promptly detected and addressed. Continuous monitoring helps organizations stay compliant with the PCI DSS requirement for regular security testing.

Compliance Reporting: DAST tools often provide comprehensive reports that detail the vulnerabilities discovered during the scanning process. These reports can be used as evidence of compliance with PCI DSS requirements for vulnerability assessments. They can demonstrate that regular testing is being conducted and identify any security gaps that need to be addressed.

Secure Development Lifecycle (SDLC): PCI DSS encourages the integration of security throughout the software development lifecycle. DAST can be incorporated into the SDLC to identify vulnerabilities early in the development process. By scanning applications during development and testing stages, organizations can catch and remediate security issues before they become more expensive and time-consuming to fix in production.

In summary, DAST is an important element for achieving PCI DSS compliance. By actively identifying vulnerabilities, offering continuous monitoring, generating compliance reports, supporting the SDLC, and assisting in risk management, DAST strengthens an organization’s security posture. Its role in enhancing security measures, safeguarding cardholder data, and ensuring adherence to PCI DSS requirements is pivotal. 

Lastly, DAST serves as an essential component within a comprehensive security strategy, enabling organizations to maintain a robust and compliant payment card environment, instilling trust among customers and stakeholders.

Mobile App Security Testing: Tools and Best Practices

Table of Content

  1. What Is Mobile Application Security Testing? 
  2. Why Is Mobile App Security Testing Important? 
  3. What Features Should a Mobile App Security Testing Tool Include? 
  4. 5 Best Practices for Security Testing in Mobile Apps 
  5. Security Testing with Bright Security

What Is Mobile Application Security Testing? 

Mobile application security testing is the process of assessing, analyzing, and evaluating the security posture of mobile applications to identify potential vulnerabilities, weaknesses, and risks. 

This testing aims to ensure the confidentiality, integrity, and availability of data and functionality in mobile applications, protecting them from unauthorized access, data breaches, and malicious activities. 

Techniques used in mobile application security testing include static analysis, dynamic analysis, penetration testing, and code review. This process helps developers to identify and address security flaws in their applications, ensuring a secure and reliable user experience across various platforms, such as Android and iOS.

In this article:

Why Is Mobile App Security Testing Important? 

Mobile app security testing is important for several reasons:

  • Data protection: Mobile apps often handle sensitive user data, such as personal information, financial details, or business data. Ensuring the security of this data is crucial to protect users from identity theft, fraud, and data breaches.
  • Compliance with regulations: Many industries have strict regulations regarding data privacy and security, such as GDPR, HIPAA, and PCI DSS. Mobile app security testing helps ensure compliance with these regulations, avoiding potential legal issues and financial penalties.
  • Reputation and trust: A secure app helps build trust with users and maintain a positive brand reputation. Security breaches can lead to loss of user trust, negative publicity, and potentially significant financial losses.
  • Competitive advantage: A secure app can differentiate itself in a crowded market, attracting users who prioritize privacy and security.
  • Reduced costs: Identifying and fixing security issues during the development process is more cost-effective than addressing them after the app is released. Mobile app security testing can help prevent costly security breaches and reduce the need for post-release patches or updates.
  • Secure development practices: Regular security testing encourages a security-focused development mindset, leading to the creation of more secure apps in the long term.
  • Device security: Mobile apps can expose not just the app itself, but also the device and other connected systems to security threats. Ensuring app security helps protect the overall device ecosystem.

What Are Mobile Application Security Testing Tools? 

Mobile application security testing tools are software programs or platforms designed to help developers and security professionals identify security vulnerabilities and weaknesses in mobile applications. These tools can be used to test mobile apps on different platforms, such as Android and iOS, and cover various aspects of security, including data protection, access control, and secure communication.

These mobile application security testing tools can help developers and security professionals identify and address security vulnerabilities in their mobile apps, ensuring a more secure user experience and protecting sensitive data.

What Features Should a Mobile App Security Testing Tool Include? 

A mobile app security testing tool should include a range of features to effectively identify and address potential security vulnerabilities. Key features to look for include:

  • Platform support: The tool should support major mobile platforms like Android and iOS, as well as any specific platforms relevant to your app.
  • Static analysis: The tool should perform static analysis by examining the source code or binary files of the app to identify potential security issues without actually executing the code.
  • Dynamic analysis: The tool should perform dynamic analysis by monitoring the app’s behavior during runtime to identify security vulnerabilities that may not be apparent during static analysis.
  • Automated testing: A good tool should automate common security testing tasks, saving time and resources while ensuring consistent and comprehensive testing.
  • Manual testing capabilities: The tool should also support manual testing, allowing security testers to perform in-depth analysis and penetration testing for more complex or targeted security concerns.
  • Integration with development tools: The tool should easily integrate with common development tools, such as integrated development environments (IDEs), build systems, and continuous integration/continuous deployment (CI/CD) pipelines, to streamline the development and testing process.
  • Customizable policies and rules: The tool should allow customization of security policies and rules to address specific organizational requirements or industry regulations.
  • Vulnerability management: The tool should provide a clear, actionable report on identified vulnerabilities, including information on the severity of the issue, potential impact, and recommendations for remediation.
  • Regular updates: A good security testing tool should be regularly updated to address new threats, vulnerabilities, and changes in the mobile app security landscape.
  • User-friendly interface: The tool should be easy to use and understand, enabling both technical and non-technical team members to participate in the security testing process effectively.
  • Scalability: The tool should be able to handle the testing of multiple apps or large, complex apps without performance issues or limitations.

Related content: Read our guide to web application scanning 

5 Best Practices for Security Testing in Mobile Apps 

1. Supply Chain Tests

Supply chain testing is a crucial aspect of mobile app security testing, as it helps identify vulnerabilities and risks associated with third-party components, such as libraries, frameworks, and APIs. 

First, ensure that you only use trusted, well-maintained, and up-to-date components from reputable sources. Perform a thorough assessment of third-party components to identify any known vulnerabilities or weaknesses. 

Additionally, monitor and track the components throughout the development lifecycle to ensure they remain secure and updated. It is essential to establish a robust governance process that includes policies, procedures, and guidelines for selecting, integrating, and managing third-party components within your mobile app development process.

2. Authentication and Authorization Testing

Authentication and authorization testing focuses on ensuring that only authorized users can access the app’s features and data. This involves verifying that the app implements strong authentication mechanisms, such as multi-factor authentication (MFA) or biometric authentication, and enforces password policies like complexity, length, and expiration. 

Authorization testing involves assessing the app’s access controls to ensure that users are granted the appropriate permissions based on their roles, and that they cannot access restricted resources or perform unauthorized actions. Regularly testing the effectiveness of your app’s authentication and authorization mechanisms helps maintain the confidentiality and integrity of sensitive data and reduces the risk of unauthorized access.

3. Encryption Testing

Encryption testing is essential for ensuring that sensitive data transmitted, stored, or processed by the app is properly protected against unauthorized access or tampering. This involves verifying that the app uses strong encryption algorithms and protocols, such as AES-256 or TLS 1.3, and that encryption keys are securely managed and stored. 

It is crucial to test encryption at various stages, including data at rest, data in transit, and data in use. Regularly reviewing and updating your app’s encryption implementation helps ensure that it remains resistant to new threats and vulnerabilities, safeguarding sensitive data and maintaining user trust.

4. Using Continuous Integration for Your Tests

Integrating security testing into your continuous integration (CI) process allows for ongoing, automated testing of the app throughout the development lifecycle. This approach helps identify and remediate security vulnerabilities early in the development process, reducing the costs and time associated with addressing them later. 

Implementing CI for security testing involves incorporating SAST, DAST, and IAST tools into your CI/CD pipeline, ensuring that security tests run automatically with each code commit or build. By regularly reviewing and refining the CI process and security test suite, developers can continuously improve the app’s security posture and maintain a security-focused development mindset.

5. Use of SAST, DAST, and IAST Techniques

Integrating static application security testing (SAST), dynamic application security testing (DAST), and interactive application security testing (IAST) techniques in the mobile app security testing process can provide comprehensive coverage and insight into potential vulnerabilities. 

SAST involves analyzing the source code or binary files of the app to identify security issues without execution. DAST involves monitoring the app’s behavior during runtime to identify vulnerabilities that may not be apparent during static analysis. 

IAST combines aspects of both SAST and DAST, providing real-time feedback on potential security risks during runtime, while also examining the code. Using these techniques in tandem allows for the identification and remediation of a wide range of vulnerabilities, ensuring a more secure mobile app.

Security Testing with Bright Security

Bright Security helps address the shortage of security personnel, enabling AppSec teams to provide governance for security testing, and enabling every developer to run their own security tests. 

NexPloit empowers developers to incorporate an automated Dynamic Application Security Testing (DAST) solution into their unit testing process so they can resolve security concerns as part of their agile development process. Bright’s DAST platform integrates into the SDLC fully and seamlessly: 

  • Test results are provided to the CISO and the security team, providing complete visibility into vulnerabilities found and remediated
  • Tickets are automatically opened for developers in their bug tracking system so they can be fixed quickly

Bright Security can scan any target, whether Web Apps, APIs (REST/SOAP/GraphQL) to help enhance DevSecOps and achieve regulatory compliance with our real-time, false positive free actionable reports of vulnerabilities. In addition, our ML-based DAST solution provides an Automated solution to identify Business Logic Vulnerabilities.

Learn more about Bright Security testing solutions

Web Application Testing: Tips & Best Practices

Table of Content

  1. What is Web Application Testing?
  2. Top Tips for Successfully Performing Web Application Testing
  3. Have Bright Do It For You

What is Web Application Testing?

Web application testing is a process that ensures the application is ready to launch without safety concerns and reliability issues. Our main point of concern in web application testing is making sure that the security is up to the standard as security becomes a bigger and bigger issue on the internet with each passing day. 

Even more importantly, properly testing your application could potentially save you thousands upon thousands of dollars, as you won’t have to deal with constant pushbacks due to security issues.

Top Tips for Successfully Performing Web Application Testing

Regardless of the size of your application, web application testing is absolutely essential in making sure you are ahead of the curve in optimizing your code. 

The first step is always to perform an in-depth analysis of your application, identify weak points, and move on from there. This will give you a general idea of the scope you are working with and you will be able to prioritize testing based on the initial test results. 

Automation is not enough

Even though automated testing is taking over nowadays, it’s usually a good idea to use some manual testing as well in order to get the full picture. The combination of the two is usually the winning approach, and as such, you will not have doubts and concerns over potential holes in your application knowing that both the human and the machine had a good hard look at it. 

Input And Output Are Crucial

For most applications, input handlers are quite often the weak point that gets exploited in all sorts of ways. This is why you have to pay special attention to both input & output in your application’s processes and test them heavily in order to make sure that nobody unauthorized can enter your application through these channels. 

Learn more in our detailed guide to penetration testing tools.

Think Like an Attacker

If you ever watched a buddy cop movie, you probably heard of the saying “think like a criminal”. Well, in this case, it applies perfectly! When testing your application, try to put yourself in a hacker’s mindset, and figure out what could be the main points of attack on your app. This will give you a different perspective, and often the more correct one, when dealing with potential vulnerabilities.

Related content: Read our guide to penetration testing in aws.

Have Bright Do It For You

If you try to follow all the correct steps in web application testing, it would probably get you a long way, but it would also take up a lot of your precious time. As we all know, time is money nowadays, which is why you probably can’t afford to spend months testing the security of your application before launching it.

This is where Bright comes in – we specialize in finding and remediating all vulnerabilities that your web application might come across. Try us out now – your application will be thanking us!