Integrating Modern DAST With DevOps

In today’s fast-paced digital landscape, the need for secure software development has never been more critical. As organizations embrace DevOps to accelerate delivery, security can no longer be an afterthought. Enter Dynamic Application Security Testing (DAST)—a modern approach to identifying vulnerabilities in running applications. When integrated seamlessly into DevOps, DAST becomes a game-changer, enabling teams to build secure software without compromising speed. In this article, we’ll explore how modern DAST tools, like Bright Security, are transforming the DevOps pipeline and why this integration is essential for businesses aiming to stay ahead of cyber threats.

Table of Content

  1. Why DevOps Needs Modern DAST
  2. Key Benefits of Integrating DAST with DevOps
  3. Bright Security: A Modern DAST Solution for DevOps
  4. Best Practices for Integrating DAST into DevOps
  5. The Future of DevOps Security
  6. Conclusion

Why DevOps Needs Modern DAST

DevOps is all about speed, collaboration, and continuous delivery. However, this rapid pace often leaves little room for traditional security practices, which are typically slow and manual. As a result, vulnerabilities can slip into production, exposing organizations to significant risks. Modern DAST tools are designed to address this challenge. By automating security testing and integrating it directly into the CI/CD pipeline, DAST ensures that vulnerabilities are identified and remediated early in the development process. This proactive approach not only enhances security but also aligns perfectly with the DevOps philosophy of continuous improvement.

Key Benefits of Integrating DAST with DevOps

Integrating DAST into DevOps enables a “shift-left” approach, where security testing occurs earlier in the development lifecycle. This reduces the cost and effort of fixing vulnerabilities later in the process. Modern DAST tools automate vulnerability scanning, allowing developers to focus on coding while the tool continuously monitors for risks. This automation ensures that security keeps pace with development.

DAST provides real-time feedback to developers, enabling them to address vulnerabilities immediately. This fosters a culture of shared responsibility for security across development and operations teams. With regulatory requirements becoming stricter, DAST helps organizations meet compliance standards by providing detailed reports and audit trails.

Bright Security: A Modern DAST Solution for DevOps

Bright Security is a cutting-edge DAST platform designed specifically for modern DevOps environments. It combines advanced vulnerability detection with seamless integration into CI/CD pipelines, making it an ideal choice for organizations looking to enhance their security posture without slowing down development.

Bright Security integrates effortlessly with popular DevOps tools like Jenkins, GitLab, and Azure DevOps, ensuring continuous security testing. Using AI and machine learning, Bright Security minimizes false positives, allowing developers to focus on real threats. With intuitive dashboards and actionable insights, Bright Security empowers developers to take ownership of security. Whether you’re a startup or an enterprise, Bright Security scales to meet your needs, providing consistent protection across all environments.

By embedding Bright Security into your DevOps pipeline, you can detect vulnerabilities in real-time during development and testing phases, reduce the risk of security breaches in production, foster collaboration between development, operations, and security teams, and achieve faster time-to-market without compromising on security.

Best Practices for Integrating DAST into DevOps

Incorporate DAST tools like Bright Security from the beginning of your project to ensure security is baked into every stage of development. Leverage automation to run DAST scans as part of your CI/CD pipeline. This ensures continuous testing without manual intervention. Train developers and operations teams on the importance of DAST and how to interpret and act on its findings. Regularly review DAST reports and use the insights to refine your development and security processes.

The Future of DevOps Security

As cyber threats continue to evolve, the integration of modern DAST tools like Bright Security into DevOps will become indispensable. By combining the speed of DevOps with the robustness of DAST, organizations can achieve a harmonious balance between innovation and security. The result? Faster, safer, and more reliable software delivery.

Conclusion

Integrating modern DAST with DevOps is no longer optional—it’s a necessity. Tools like Bright Security are leading the charge, enabling organizations to build secure applications at the speed of DevOps. By embracing this integration, businesses can stay ahead of cyber threats, meet compliance requirements, and deliver high-quality software that users can trust.

Ready to revolutionize your DevOps pipeline? Explore Bright today and take the first step toward a more secure future.

Why Broken Crystals Is an Ideal Testing Ground for AST Solutions

Application Security Testing (AST) plays a pivotal role in identifying vulnerabilities during the software development lifecycle. However, its efficacy depends on having a comprehensive and realistic testing environment. Broken Crystals, an intentionally vulnerable and open-source web application, is an outstanding testing ground for AST solutions. Built to simulate modern vulnerabilities, it provides security professionals and developers with a safe and controlled platform to refine their tools and techniques.

Table of Content

  1. The Purpose of Broken Crystals
  2. How Broken Crystals Enhances AST Testing
  3. Benefits of Using Broken Crystals Over Alternatives
  4. How Organizations Can Leverage Broken Crystals
  5. Conclusion

The Purpose of Broken Crystals

Broken Crystals was created with one primary goal: to offer a realistic, open-source environment for testing and training in application security. Unlike production systems, where experimenting with security tools can be risky, Broken Crystals allows users to test AST tools without jeopardizing live applications or sensitive data. This web application is intentionally embedded with vulnerabilities such as SQL injection, cross-site scripting (XSS), insecure direct object references (IDOR), and more, reflecting the complexities of modern web applications.

How Broken Crystals Enhances AST Testing

Broken Crystals stands out as a testing ground for AST solutions for several key reasons:

Realistic Vulnerabilities

Broken Crystals mirrors the architecture and vulnerabilities of modern web applications, including API-heavy interactions and client-server architectures. It provides a practical environment for AST solutions to detect issues such as input validation flaws, authentication misconfigurations, and insecure API endpoints.

Safe and Controlled Environment

Testing AST tools on live applications can lead to unintended disruptions or expose sensitive data. Broken Crystals mitigates these risks by offering a sandbox environment where users can run scans, validate results, and fine-tune configurations without worry.

API Vulnerability Testing

In addition to web-based vulnerabilities, Broken Crystals includes APIs with built-in weaknesses, enabling AST solutions to test their capabilities in identifying API-specific issues like insufficient authentication, token manipulation, and rate-limiting flaws.

Immediate Feedback

Broken Crystals provides transparency by enabling users to compare AST results against known, intentionally embedded vulnerabilities. This makes it easy to evaluate tool effectiveness, identify detection gaps, and adjust configurations as needed.

Training Opportunities

For organizations adopting a DevSecOps approach, Broken Crystals serves as a valuable training resource. Developers and security teams can learn about vulnerabilities, practice using AST tools, and prioritize remediation strategies in a hands-on environment.

Benefits of Using Broken Crystals Over Alternatives

While several intentionally vulnerable applications exist, such as OWASP Juice Shop, Broken Crystals offers distinct advantages:

Modern Vulnerabilities and Technologies

Many testing environments feel outdated, focusing on vulnerabilities that are less common in today’s software landscape. Broken Crystals emphasizes challenges found in modern web applications, such as API-heavy architectures, cloud-native technologies, and client-server interactions.

Open Source and Accessibility

Broken Crystals is open source, ensuring accessibility for teams of all sizes and technical expertise. This ease of deployment allows organizations to quickly set up a testing environment without significant barriers.

Scalability for AST

Unlike alternatives such as OWASP Juice Shop, which cater more to training and manual testing, Broken Crystals is designed to support automated testing at scale, making it ideal for AST tools.

How Organizations Can Leverage Broken Crystals

Tool Evaluation

Organizations can use Broken Crystals to evaluate and compare different AST solutions, assessing factors like vulnerability coverage, false positive rates, and ease of integration.

Configuration Optimization

Broken Crystals allows users to fine-tune AST tool settings, ensuring a balance between comprehensive vulnerability detection and minimal false positives.

Training and Awareness

Security teams and developers can run scans on Broken Crystals, analyze the results, and work through remediation steps. This hands-on approach builds a deeper understanding of both vulnerabilities and AST capabilities.

Performance Benchmarking

Organizations can test the scalability and performance of AST tools by running them against Broken Crystals under various simulated conditions, such as high traffic or concurrent scans.

Conclusion

Broken Crystals is more than just an intentionally vulnerable web application; it is a comprehensive, modern, and scalable resource for AST solutions. Its realistic vulnerabilities, focus on modern technologies, open-source nature, and scalability for automated testing make it an invaluable tool for organizations seeking to enhance their application security practices. By leveraging Broken Crystals, teams can optimize their AST tools, gain critical training, and build a proactive security posture tailored to the complexities of today’s digital landscape.

The Illusion of Security: Why Relying Solely on WAF is a Bad Practice

Our security research team has been looking into the security of WAF applications and discovered a concerning trend: while WAFs (Web Application Firewalls) are effective at blocking certain types of known threats, they are not a panacea. Many organizations rely solely on WAFs as a shield, assuming their applications are secure without further testing. This assumption leaves critical runtime vulnerabilities undetected.

WAFs operate based on predefined rules and signatures, which makes them powerful against known attacks but inadequate when it comes to zero-day threats or sophisticated attack vectors that don’t fit traditional patterns. They can’t fully simulate dynamic user interactions or detect issues that arise from complex workflows within an application.

To build a truly secure environment, organizations must complement WAFs with thorough dynamic testing strategies, like DAST. DAST goes beyond signature matching to probe the application as it runs, uncovering vulnerabilities that a WAF might miss entirely. This combination ensures robust defense and reduces the risk of security breaches.

Table of Content

  1. A story from the team:
  2. The Role of WAF in Security
  3. The Limitations of WAF
  4. Real life examples:
  5. The Importance of Updating Technologies
  6. The Necessity of Security Testing
  7. Secure Coding Practices
  8. Conclusion

A story from the team: 

Recently, Bright’s security team uncovered significant vulnerabilities in a major corporation with over $150 billion in revenue. The company, which utilises AngularJS and Akamai WAF, was found to be susceptible to prototype pollution, HTML injection leading to Open Redirect, and cross-site scripting (XSS) attacks. These vulnerabilities highlight a critical flaw in the company’s security strategy: an overreliance on WAF without adequate emphasis on secure coding practices, technology updates, and insufficient application-level security testing and scanning.

The lack of thorough application-level security testing and scanning is a significant issue. Many organisations rely heavily on perimeter defences like WAFs, which can miss vulnerabilities within the application itself. Application security testing tools, such as Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST), are essential because they help identify and remediate vulnerabilities in the source code and running applications respectively​.

Without these tools, companies may fail to detect critical vulnerabilities early in the development process, leaving them exposed to potential exploits. This can lead to significant risks, including data breaches, financial loss, and damage to reputation. Furthermore, integrating security testing into the software development lifecycle (SDLC) allows developers to address issues promptly, reducing the overall cost and effort required for remediation​.

By not conducting sufficient application-level security testing, the organisation increases the likelihood that vulnerabilities will go undetected until they are exploited by attackers.

The Role of WAF in Security

Web Application Firewalls are designed to filter and monitor HTTP traffic between a web application and the Internet. They protect against common attacks such as SQL injection, XSS, and other OWASP Top 10 threats. While WAFs are an important layer of defence, they are not a silver bullet. WAFs can only protect against known vulnerabilities and attack patterns. They cannot defend against new, sophisticated, or zero-day attacks that exploit unknown vulnerabilities.

The Limitations of WAF

1. False Sense of Security: Relying solely on WAF can create a false sense of security. Organisations may neglect other essential security measures, assuming the WAF will catch all threats.

2. Bypass Techniques: Attackers continuously develop techniques to bypass WAF protections. This makes it critical to have additional layers of security. For example:

  • Encoding and Obfuscation: Attackers often use sophisticated encoding techniques to disguise malicious payloads, making them difficult for WAFs to detect. For example, URL encoding and Base64 encoding can transform a payload into a format that bypasses WAF filters​.
  • HTTP Parameter Pollution: By injecting multiple parameters with the same name, attackers can confuse WAFs, causing them to miss malicious content. This technique exploits how different components of the application process input parameters differently​.
  • Behavioral and Machine Learning Limitations: Even advanced WAFs that use machine learning (ML) can be bypassed. Attackers can train their payloads to mimic legitimate traffic patterns, thereby evading detection. For instance, modifying attack patterns slightly or interspersing benign data with malicious code can trick ML-based WAFs. ML models can suffer from high rates of false positives and negatives. This means that they might block legitimate traffic (false positives) or allow malicious traffic (false negatives), especially when attackers craft payloads to appear as normal behaviour.
  • Unknown Vulnerabilities: WAFs rely on known signatures and patterns to detect attacks. However, zero-day exploits, which target unknown vulnerabilities, can bypass WAF protections entirely. Attackers constantly discover new vulnerabilities that WAFs have not yet been trained to recognize, making it easy to bypass them using fresh, undiscovered exploits​

Real life examples:

1. Cloudflare WAF Bypass Leading to Reflected XSS:

  • Blocked Payload: “>
  • Bypass Payload: “>
  • Explanation: The initial payload was blocked by Cloudflare, but by modifying the onerror attribute to include an additional, seemingly harmless attribute (onerrora=confirm()), the WAF was bypassed, resulting in a successful XSS attack when the second onerror executed.

2. Akamai WAF Bypass:

Click here

3. Performance Overhead: WAFs can introduce latency and impact application performance, which might lead to trade-offs between security and user experience.

4. Limited Scope: WAFs primarily focus on web traffic and do not address underlying vulnerabilities in the code or application logic.

The Importance of Updating Technologies

In the case of the corporation mentioned earlier, their use of AngularJS, a framework that is no longer actively maintained, contributed to their vulnerabilities. Modern frameworks like Angular (the successor to AngularJS) offer improved security features and regular updates to address emerging threats. Sticking with outdated technologies exposes applications to known vulnerabilities that attackers can exploit easily.

The Necessity of Security Testing

Regular security testing, including static code analysis (SAST), dynamic analysis (DAST), and penetration testing, is essential to identify and remediate vulnerabilities. Security testing should be an integral part of the software development lifecycle (SDLC). Common automated tools usually aim for the long hanging fruits while missing the business logic vulnerabilities and multi-step attacks. However, as these tools evolve, they are increasingly aiming to address more sophisticated attack vectors, including multi-step exploits. Over time, advancements in automation will enable these tools to detect a wider array of vulnerabilities, potentially covering most, if not all, intricate attack scenarios.

Secure Coding Practices

Implementing secure coding practices is fundamental to building secure applications. Developers should be trained in secure coding principles and best practices, such as:

  • Input validation and sanitization
  • Proper error handling
  • Least privilege principle
  • Regular code reviews and audits

Conclusion

Relying solely on WAF for security is a perilous strategy. While WAFs are an important component of a comprehensive security strategy, they should not be the only line of defence. Organisations must prioritise updating their technologies, conducting regular security testing, and fostering a culture of secure coding. By doing so, they can build resilient applications that withstand the evolving threat landscape and protect their valuable assets and reputation.

For the corporation with over $150 billion in revenue, the vulnerabilities discovered underscore the need for a more holistic approach to security. Investing in modern technologies, continuous security testing, and secure development practices is not just advisable—it’s essential for safeguarding the future.

By addressing these fundamental aspects of security, organisations can move beyond the illusion of security provided by WAFs and build robust defences against the ever-growing array of cyber threats.

The Hidden Costs of Ignoring DAST in Agile Development

In the fast-paced world of Agile development, speed is often the primary objective. Teams push through development cycles rapidly, releasing features at an impressive pace. However, in the race to deliver quickly, one critical aspect frequently gets overlooked: Dynamic Application Security Testing (DAST). This oversight isn’t a trivial matter but a serious issue with hidden costs that can jeopardize your project’s success.

Table of Content

  1. The Mirage of Speed
  2. Financial Consequences of Security Breaches
  3. Erosion of Customer Trust
  4. Productivity Challenges
  5. Regulatory Compliance Risks
  6. Competitive Disadvantage
  7. Accumulating Technical Debt
  8. The False Sense of Security
  9. Impact on Team Morale
  10. The Escalating Cost of Late Fixes
  11. Conclusion

The Mirage of Speed

Agile development promises rapid delivery, but speed without security can lead to disaster. Skipping essential security testing might initially seem like a time-saving move. However, undetected vulnerabilities can persist, eventually causing security breaches that require extensive rework and resource reallocation. Identifying and addressing runtime vulnerabilities early keeps development on track, ensuring smooth progress without expensive interruptions.

Financial Consequences of Security Breaches

Security breaches are costly—sometimes disastrously so. The immediate financial repercussions may include legal fees, customer notifications, and regulatory fines, but these are just surface-level expenses. The deeper, more damaging consequences involve lost business, a tarnished reputation, and customer churn. Investing in early security measures is a modest expense compared to the financial devastation a breach can cause.

Erosion of Customer Trust

Customer trust is invaluable but fragile. A single security lapse can convey to users that their data is not safe, causing a swift loss of loyalty. Conducting regular security assessments helps identify and patch vulnerabilities before they can be exploited. This proactive approach reassures customers that their information is protected, fostering long-term trust and confidence.

Productivity Challenges

Skipping security tests might appear to boost productivity, but this is deceptive. The time saved by avoiding tests is quickly overshadowed by the extensive time required to address security incidents. Proactive security testing keeps development pipelines running smoothly, freeing teams from constant fire drills and enabling them to meet deadlines without burning out.

Regulatory Compliance Risks

Laws and regulations like GDPR and CCPA are more than bureaucratic formalities—they are legal obligations. Failure to comply can lead to severe fines and penalties. Security assessments help ensure adherence to these regulatory frameworks, transforming potential compliance nightmares into manageable tasks.

Competitive Disadvantage

Security can be a significant differentiator in a crowded market. Applications known for robust security are more likely to attract and retain users. Strengthening your application against threats positions you as a trustworthy choice, giving you a competitive edge over less security-conscious rivals.

Accumulating Technical Debt

Ignoring vulnerabilities is akin to accruing technical debt—one that accumulates interest over time. The longer these vulnerabilities remain unaddressed, the more complex and costly they become to resolve. Proactively fixing vulnerabilities keeps technical debt manageable and prevents issues from escalating.

The False Sense of Security

Relying solely on other testing methods can create a false sense of security. Static Application Security Testing (SAST) may identify code flaws, but it cannot detect runtime vulnerabilities. Comprehensive security testing that includes DAST provides a more holistic view of potential threats, offering stronger protection.

Impact on Team Morale

Security breaches can demoralize developers. The satisfaction of delivering a new feature is often overshadowed by the stress of potential vulnerabilities. Regular security testing and a security-conscious culture empower developers, boosting their confidence and sense of accomplishment.

The Escalating Cost of Late Fixes

The cost to fix a vulnerability increases exponentially the later it is detected in the development cycle. Early identification and remediation ensure more cost-effective fixes, reducing both financial and operational burdens.

Conclusion

In the relentless pursuit of Agile development, security should never be sacrificed. Ignoring essential security measures like DAST comes with hidden costs too significant to overlook. By integrating dynamic security testing into your development processes, you are not only safeguarding your application but also ensuring the long-term success of your project. In development, it’s always wiser to tread carefully and securely than to stumble over unforeseen obstacles.

Enterprise Grade DAST vs Other DAST Solutions

Dynamic Application Security Testing (DAST) tools are essential for identifying vulnerabilities in applications during runtime. However, not all DAST tools are created equal. Enterprise-grade DAST solutions are designed to meet the complex and high-stakes needs of large organizations, setting them apart from more basic or developer-focused options. One of their most significant advantages is the ability to test business logic vulnerabilities while offering advanced authentication and crawling capabilities, making them indispensable for modern enterprises.

Table of Content

  1. The Unique Demands of Enterprise Security
  2. Choosing the Right DAST for Your Enterprise
  3. Conclusion

The Unique Demands of Enterprise Security

Large enterprises often deal with highly complex environments that include diverse applications, numerous APIs, and globally distributed teams. In such scenarios, a DAST tool needs to do more than just detect vulnerabilities. It must integrate seamlessly with existing workflows, provide actionable insights, and scale effectively across multiple teams and projects. Enterprise-grade DAST tools excel in these areas and address challenges that simpler tools cannot.

1. Scalability and Performance

Enterprise environments typically include hundreds, if not thousands, of applications and APIs that need regular security assessments. Enterprise-grade DAST solutions are designed to handle such scale efficiently by supporting:

  • Parallel Scans: The ability to run multiple scans simultaneously without a performance dip.
  • Large Workloads: High-speed scanning to process large applications and extensive endpoints quickly.

In contrast, basic DAST tools often struggle with performance when applied to enterprise-scale use cases, leading to delays and bottlenecks.

2. Advanced Customization and Configuration

Enterprise-grade DAST tools offer organizations the flexibility to tailor scans to their unique requirements. They support advanced configurations such as:

  • Custom test cases for unique application architectures.
  • Fine-grained scanning controls for specific endpoints or APIs.
  • Role-based access for managing users across distributed teams.

Basic tools often lack these options, making them unsuitable for testing applications with non-standard architectures or complex workflows.

3. Integration with Enterprise Workflows

Seamless integration with DevSecOps pipelines and enterprise tools is another major differentiator for enterprise-grade DAST solutions. They provide:

  • CI/CD Compatibility: Easy integration with Jenkins, GitLab, Azure DevOps, and other CI/CD tools.
  • Comprehensive Reporting: Support for export formats (e.g., JSON, CSV, XML) compatible with third-party security management systems.
  • API Access: Robust APIs to automate scans and integrate results into broader workflows.

Basic tools often lack robust APIs or CI/CD integration, limiting their usefulness in fast-paced DevSecOps environments.

4. Broader Vulnerability Detection

One of the most significant advantages of enterprise-grade DAST tools is their ability to identify business logic vulnerabilities – issues that arise from flaws in the design or implementation of application workflows. These tools also:

  • Detect advanced issues such as server-side request forgery (SSRF).
  • Perform compliance-focused scans for regulations like PCI DSS or GDPR.
  • Handle complex applications with multi-step authentication and dynamic content.

In contrast, basic DAST tools typically focus on common vulnerabilities like SQL injection or cross-site scripting (XSS), leaving critical enterprise issues undetected.

5. Comprehensive Reporting and Insights

Enterprise-grade DAST tools provide detailed and actionable reports to help teams prioritize vulnerabilities effectively. Key features include:

  • Risk Scoring: Helps teams focus on the most critical vulnerabilities.
  • Granular Reports: Segmented by application, team, or compliance standard.
  • Developer-Friendly Guidance: Often includes links to code snippets or remediation steps.

Basic tools may only offer generic or high-level reports, which are less helpful for large teams working across multiple projects.

6. Continuous Support and Updates

With new threats emerging daily, enterprise-grade DAST tools prioritize timely updates and active support. These include:

  • Real-Time Threat Intelligence: Identifies the latest attack vectors.
  • Dedicated Support Teams: Rapidly resolve technical issues.
  • Regular Updates: Ensures scanning algorithms and compliance libraries stay current.

Basic DAST tools often lack the same level of ongoing support, leaving enterprises vulnerable to evolving threats.

Choosing the Right DAST for Your Enterprise

While enterprise-grade DAST solutions offer significant advantages, they come at a higher cost and require more time to implement effectively. Organizations should evaluate their needs carefully, considering factors such as:

  • Scale: How many applications or APIs require regular scanning?
  • Complexity: Are there unique configurations or multi-layered applications that need advanced testing?
  • Integration Needs: Does the solution need to fit seamlessly into existing CI/CD pipelines or security ecosystems?

For small or mid-sized teams with simpler applications, basic DAST tools might suffice. However, for enterprises managing mission-critical applications in a complex environment, an enterprise-grade solution is often the only viable choice.

Conclusion

Enterprise-grade DAST tools go far beyond the basic functionality of standard DAST solutions, offering scalability, customization, and advanced integrations to meet the demands of large organizations. With the ability to test business logic vulnerabilities, leverage advanced authentication mechanisms, and provide robust crawling capabilities, they empower enterprises to secure complex, dynamic applications and APIs while aligning with modern DevSecOps practices. By investing in enterprise-grade DAST, organizations can ensure they stay ahead of evolving threats and maintain a strong security posture across their digital ecosystems.

Why You Should Use DAST to Scan Microservices

In today’s digital age, microservices have revolutionized software development by enabling teams to build scalable and flexible applications. This architectural style involves dividing a system into smaller, independent services that can be developed, deployed, and scaled individually. However, the adoption of microservices comes with its own set of challenges, particularly around security. With each service functioning as a standalone entity, the attack surface expands significantly, increasing the likelihood of vulnerabilities. Dynamic Application Security Testing (DAST) offers an effective way to address these challenges by identifying vulnerabilities in running applications, making it a critical tool for securing microservices.

Table of Content

  1. Understanding DAST and Microservices
  2. Benefits of Using DAST for Microservices
  3. Why DAST Outshines SAST for Microservices
  4. Implementing DAST in Microservices Security
  5. Conclusion

Understanding DAST and Microservices

DAST is a black-box testing method that evaluates the security of an application by simulating attacks on it while it is running. Unlike Static Application Security Testing (SAST), which analyzes source code, DAST operates on deployed applications. This dynamic approach makes DAST especially effective for microservices, where the security of APIs, runtime environments, and inter-service communication must be tested in real-world conditions.

Microservices are often exposed through APIs, making them susceptible to attacks like injections, insecure direct object references (IDOR) and other business logic attacks. DAST tools can probe these APIs to uncover vulnerabilities that might be missed during static analysis. Moreover, because microservices communicate over a network, runtime security issues such as misconfigured headers, insufficient encryption, or broken authentication mechanisms are critical to address—all areas where DAST excels.

Benefits of Using DAST for Microservices

  1. Real-World Testing DAST operates on running applications, simulating the perspective of an attacker. This is particularly important for microservices, where vulnerabilities often arise in runtime configurations, API endpoints, and inter-service communication. Unlike SAST, which evaluates code in isolation, DAST reveals how these components behave under real-world conditions.
  2. Comprehensive Coverage Modern microservices-based architectures rely heavily on APIs, often involving complex chains of requests and responses. DAST tools can systematically test these APIs to ensure that they are secure against injection attacks, unauthorized access, and other vulnerabilities. Additionally, DAST can analyze web interfaces and service endpoints for misconfigurations or exposed data.
  3. Language and Framework Agnostic Microservices are typically built using a variety of languages and frameworks. Because DAST does not depend on source code, it can scan applications regardless of the technologies used, ensuring consistent security testing across heterogeneous environments.
  1. Detection of Configuration Issues Microservices often require various runtime configurations, such as environment variables, SSL certificates, and load balancers. Misconfigurations can lead to vulnerabilities that SAST tools might miss because they don’t analyze deployed environments. DAST can identify such issues in real-world deployments.

Why DAST Outshines SAST for Microservices

While both DAST and SAST are important components of a comprehensive security strategy, DAST has distinct advantages when it comes to microservices.

  1. Runtime Context SAST analyzes code in a static state, making it unable to account for runtime variables, configurations, or external dependencies. DAST, on the other hand, operates in the application’s runtime environment, uncovering issues that only manifest when the application is live. For example, SAST may miss a vulnerability caused by a misconfigured API gateway, whereas DAST can detect it during a scan.
  2. Focus on APIs and Endpoints Since microservices rely heavily on APIs for communication, securing these interfaces is critical. While SAST can analyze the code that defines API behavior, it cannot validate how APIs function in a deployed state. DAST excels in testing API endpoints for common vulnerabilities like broken authentication, weak encryption, and data leakage.
  3. Technology Agnostic In a microservices ecosystem, teams often use diverse programming languages and frameworks. SAST tools require language-specific analyzers, which can limit their applicability. DAST, being technology agnostic, can scan the entire ecosystem, regardless of the underlying codebase.
  4. Uncovering Logical Vulnerabilities Logical vulnerabilities, such as improper handling of user input or flawed authentication workflows, are often undetectable by SAST. DAST simulates real-world scenarios to identify such vulnerabilities. For example, DAST can detect that a user can bypass a security check by manipulating a session token—something that SAST would not identify from static code analysis.
  5. Reduced False Positives One of the challenges with SAST is the high number of false positives, which can overwhelm developers and slow down remediation efforts. DAST, by testing the live application, reduces false positives significantly. Vulnerabilities identified by DAST are real and exploitable, making them more actionable for security teams.
  6. Cost-Effectiveness SAST often requires significant effort to configure and integrate with diverse codebases. Additionally, fixing issues identified during static analysis can be time-consuming and expensive, especially if vulnerabilities are found late in the development cycle. DAST simplifies this process by identifying exploitable vulnerabilities in real-world scenarios, allowing teams to prioritize fixes effectively.

Implementing DAST in Microservices Security

To maximize the benefits of DAST, organizations should follow best practices when implementing it in their security workflows:

  1. Automate DAST Scans Integrate DAST tools into the CI/CD pipeline to ensure continuous security testing. Automation reduces manual effort and ensures that every deployment is tested for vulnerabilities.
  2. Complement with SAST While DAST is superior for runtime testing, SAST still plays a vital role in identifying vulnerabilities during the development phase. Using both tools ensures comprehensive coverage.
  3. Test in Staging Environments Run DAST scans in staging environments that closely mimic production. This allows teams to identify and fix vulnerabilities before they affect end users.
  4. Focus on High-Risk Areas Prioritize scanning APIs and endpoints that handle sensitive data or perform critical functions. These areas are often the primary targets for attackers.
  5. Analyze Results and Iterate Use the insights from DAST scans to continuously improve the security of your microservices. Share findings with developers to foster a culture of security awareness.

Conclusion

Microservices have transformed the way modern applications are built and deployed, but they also introduce new security challenges. DAST is uniquely positioned to address these challenges by testing running applications in real-world conditions. Its ability to uncover runtime vulnerabilities, test APIs, and provide actionable insights makes it indispensable for securing microservices. While SAST has its place in the development lifecycle, DAST outshines it when it comes to runtime testing, reducing false positives, and ensuring comprehensive security in diverse environments.

By integrating DAST into your security strategy, you can safeguard your microservices architecture, protect sensitive data, and maintain user trust in an increasingly complex digital landscape.

IASTless IAST: The SAST to DAST Bridge

In the ever-evolving landscape of application security testing, the pursuit of a more efficient and streamlined approach is a constant endeavor. With the challenges posed by traditional Interactive Application Security Testing (IAST) methodologies, a new paradigm is emerging – one that eliminates the complexities associated with IAST deployment while enhancing the synergy between Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST). Welcome to the world of “IASTless IAST – The SAST to DAST Bridge.”

Table of Content

  1. What is SAST:
  2. What is DAST:
  3. What is IAST:
  4. The IAST Conundrum:
  5. Bridging the Gap with Bright’s Dev-Centric DAST:
  6. (Bright’s DAST + SAST) > IAST:
  7. Advantages of IASTless IAST:
  8. Implementing IASTless IAST:
  9. Conclusion

What is SAST:

SAST (Static Application Security Testing) is a static analysis methodology that examines the source code, bytecode, or binary code of an application for security vulnerabilities without executing the program. Its strengths include early detection of issues in the development lifecycle, but drawbacks include false positives, limited coverage of runtime behaviors, and challenges in handling complex and dynamic code.

What is DAST:

DAST (Dynamic Application Security Testing) is a security testing method that evaluates an application in its running state by simulating real-world attacks. Its advantages include a realistic assessment of security vulnerabilities in the live environment, but potential downsides are limited visibility into source code and later detection potential in the SDLC as it needs a running target.

What is IAST:

IAST (Interactive Application Security Testing) is a security testing methodology that analyzes applications in real-time during runtime, providing dynamic insights into vulnerabilities and potential security threats. Its benefits include real-time detection of vulnerabilities, reduced false positives, and the ability to assess an application’s security posture during actual usage.

IAST is meant to introspect the application’s flow in real-time usage and should be able to give information about which path in the program and code did the relevant payloads or attacks took until they reach the part of the vulnerable code.

The IAST Conundrum:

Traditional IAST solutions have long been plagued by intricate deployment processes, runtime tracing requirements, and the need for extensive support for complex frameworks. Additionally, generating traffic for IAST often demands full Quality Assurance (QA) automation or comprehensive end-to-end (e2e) automated testing coverage. These challenges have led security practitioners to seek a more efficient and effective approach that aligns with the dynamic nature of modern application development.

Bridging the Gap with Bright’s Dev-Centric DAST:

By leveraging DAST’s capability to scan applications in runtime without the need for exhaustive setup, organizations can sidestep the hurdles associated with IAST. Bright’s DAST provides a comprehensive assessment of an application’s security posture without requiring the meticulous instrumentation and runtime tracing that IAST demands.

(Bright’s DAST + SAST) > IAST:

In the IASTless IAST approach, we’re threading a practical integration between Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST), steering clear from the conventional reliance on Interactive Application Security Testing (IAST) for runtime analysis. Here, organizations can harness their existing SAST solutions in tandem with Bright’s DAST. This collaboration gets a technical boost from Bright’s SAST Validation logic.

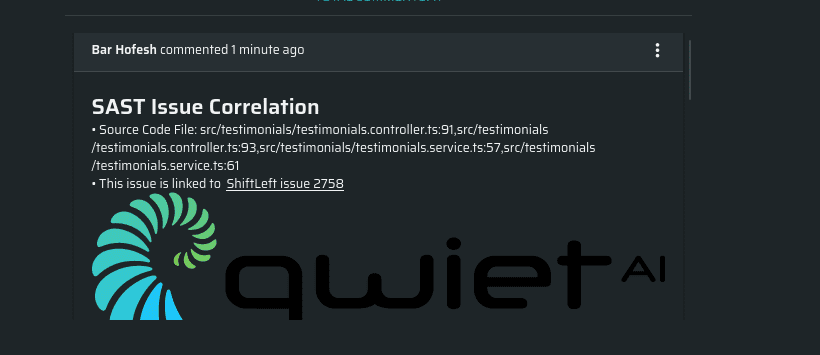
image-20240204-112312.png

This isn’t just about cross-checking and correlation; it’s about handing developers a nuanced technical insight that’s often missing in IAST-centric setups. The SAST to DAST bridge pulls back the curtain, offering a ground-level view—from External Request to Internal Source Code. This technical tweak allows developers to pinpoint the specific request that flags a vulnerability and directly tie it to a file within the source code. It taps into the detailed insights provided by SAST, bringing a hands-on understanding of security issues.

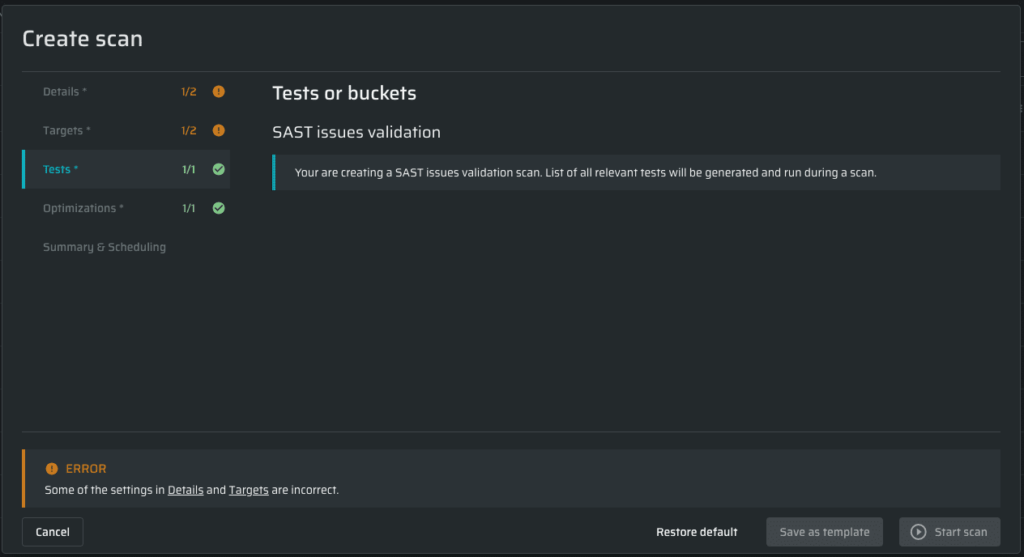
image-20240204-112340.png

Simply put, this technical maneuver equips developers with a more precise perspective on the security landscape. It lets them dive into the nitty-gritty details of vulnerabilities at a code level, making decisions rooted in technical understanding. The SAST and DAST synergy not only beefs up the technical efficiency of security assessments but also fosters a collaborative atmosphere between development and security teams, embodying the technical essence of the IASTless IAST methodology.

Advantages of IASTless IAST:

  1. Simplified Deployment: Say goodbye to the intricacies of IAST deployment. IASTless IAST streamlines the security testing process, making it more accessible and manageable for development teams.
  2. Reduced Overhead: Eliminate the need for continuous runtime tracing and complex instrumentation. The collaboration between SAST and DAST minimizes the overhead associated with traditional IAST solutions.
  3. Cost-Effective: Leveraging existing SAST investments alongside Bright’s DAST results in a cost-effective approach to application security. No need for additional tools or extensive training.
  4. Enhanced Accuracy: Correlating SAST and DAST findings provides a more comprehensive view of potential vulnerabilities, enhancing the accuracy of security assessments.

Implementing IASTless IAST:

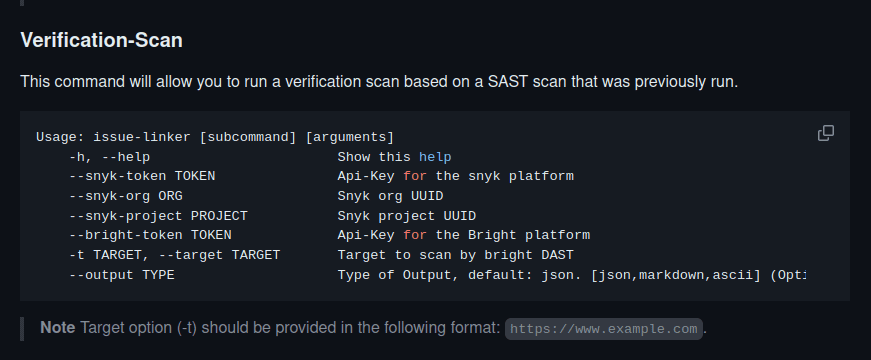
To seamlessly incorporate the IASTless IAST approach into your application security workflow, leverage the power of Bright’s IssueLinker—a sophisticated CLI tool designed for correlating and validating SAST results with Bright’s DAST through straightforward configurations. The integration of this tool introduces a level of professionalism and efficiency, ensuring a seamless collaboration between SAST and DAST findings.

Explore the capabilities of Bright’s IssueLinker to effortlessly link and correlate security vulnerabilities identified by your SAST solutions with Bright’s dynamic assessments. This command-line interface tool provides a user-friendly experience, allowing security teams to validate and prioritize findings efficiently.

Furthermore, Bright facilitates in-app integration with various SAST solutions through its “SAST Validation” organization configuration. This feature, documented in detail in the Bright documentation, streamlines the process of cross-referencing static and dynamic security findings, offering a professional and comprehensive security validation solution.

By incorporating Bright’s IssueLinker and exploring in-app integrations, organizations can establish a robust IASTless IAST framework that not only simplifies the security testing process but also elevates the overall professionalism of the application security workflow. This comprehensive implementation ensures that the correlation and validation of SAST and DAST findings align seamlessly, providing a detailed and accurate assessment of your application’s security posture.

Conclusion:

The IASTless IAST approach represents a paradigm shift in application security, offering a more pragmatic and efficient alternative to traditional IAST methodologies and driving additional value from both your SAST and DAST solutions. By leveraging the strengths of both SAST and Bright’s DAST, organizations can achieve a comprehensive and accurate understanding of their application security posture, while significantly reducing time wasted evaluating false positives. In addition this approach simplifies deployment and minimizes operational overhead. It’s time to bridge the gap between static and dynamic testing and embrace a more streamlined and effective approach to securing modern applications.

Broken Access Control: Attack Examples and 4 Defensive Measures

Last reviewed and updated: June 2026

AI-generated code is basically the holy grail of developer tools of this decade. Think back to just over two years ago; every third article discussed how there weren’t enough engineers to answer demand; some companies even offered coding training for candidates wanting to make a career change. The demand for software and hardware innovation was only growing, and companies were asking themselves, with increasing concern, “How do we increase velocity?” Then OpenAI came out with ChatGPT, and all of a sudden, LLMs and AI-powered tools and platforms were everywhere. One of which is AI-generated code. 

In this post, I will walk you through security in the context of AI-generated code and show you a live example of how DAST security testing can be applied to AI-generated code. 

Table of Content

  1. Not all code is created equal 
  2. This isn’t a theoretical problem
  3. Enter AI-generated security vulnerabilities on steroids 
  4. Bright for Copilot 
  5. Emerging security threats in AI-generated code

Not all code is created equal 

If it looks like a duck and quacks like a duck, is it a duck? Or, in the case of AI-generated code, if it looks like code and runs like code, is it good code? One of the most common misconceptions regarding Generative AI, and LLMs in particular, is that they understand the questions they are being asked and apply the same reasoning to their answer as a person would. However, the only thing that these models do is predict the answer, be it question-answering or code completion, based on their training data. Unlike their traditional machine learning model counterparts, whose training data is meticulously gathered, cleaned, and vetted, Gen AI models are basically trained on the entire web and more (if available in proprietary datasets, for example). 

In the case of AI-generated code, this means that the training data is basically all publicly accessible code repositories, documentation, and examples – the good, the bad, and the ones riddled with security vulnerabilities. Bottom line, while LLMs, for the most part, will sound correct, knowledgeable, and confident in their answers, they are not “thinking” what would be the best completion of your code, only predicting a completion based on what they have seen previously in the wild. 

This isn’t a theoretical problem

In the StackOverflow 2023 survey, over 82% of the respondents currently use AI tools to write code, and 42% answered that they trust the accuracy of the output, while 31% are on the fence.

According to Gartner, 75% of enterprise software engineers are expected to use AI coding assistants by 2028. Thus, we can expect that not only will code and release velocity increase but that organizations’ overall code volume will also increase. 

Enter AI-generated security vulnerabilities on steroids 

First, let’s differentiate between LLM security issues and LLM-generated software or application security issues.

  • LLM security vulnerabilities are manipulations of a deployed LLM, say in an AI-powered chatbot on your website, to get it to provide access to restricted data or operations. Typically, prompt engineering and guardrails will be applied here to test and safeguard the model, but this should also be tested on the application level. 
  • LLM-generated software or application security vulnerabilities include code, web, API, and business logic security vulnerabilities. 

In the case of code generation, most vulnerabilities will fall under LLM-generated software or application security vulnerabilities, but AI-generated code is 4X more prone to security vulnerabilities, according to Gartner. With the overall volume of code only increasing, this is further compounding existing issues such as security testing happening too late in the SDLC and the need for more shift-left testing, developers working in different tools than AppSec, and not always having the necessary security knowledge needed to resolve security vulnerabilities. 

This is where Bright’s security unit testing extension comes into play. 

Bright for Copilot 

Bright’s LLM-powered security unit testing extension for GitHub Copilot helps organizations accelerate code generation without introducing security vulnerabilities. It puts DAST in the hands of developers at the IDE and unit testing levels, letting them leverage security testing from the get-go without having to become security gurus.

Emerging security threats in AI-generated code

AI-generated code will not be going anywhere. On the contrary, developers are already using it in mass in individual plans, if not organizational settings. If history teaches us anything, it is that when developers adopt engineering tools from the grassroots, it is only a matter of time before they make it into the enterprise. The benefits for both are abundantly clear, greater productivity and velocity. 

That said, AI-generated code is a brand new attack surface that modern enterprises need to evaluate and safeguard. That is why Bright is developing extensions and capabilities geared to empower developers to do security testing throughout their SDLC and across new evolving attack surfaces.

Vulnerability Scanners: 4 Key Features, Types, and How to Choose

Table of Content

  1. What Is a Vulnerability Scanner? 
  2. Key Features of Vulnerability Scanners 
  3. Types of Vulnerability Scanners 
  4. How to Choose a Vulnerability Scanner Tool 

What Is a Vulnerability Scanner? 

A vulnerability scanner is a specialized software tool designed to assess the security of computers, networks, or applications by automatically detecting and analyzing weaknesses. These scanners proactively search for security vulnerabilities, such as unpatched software, misconfigurations, and other security gaps that could be exploited by attackers. Some scanners can simulate the actions of an attacker to help identify exploitable vulnerabilities.

Vulnerability scanners are essential in the cybersecurity toolkit, providing ongoing insight into the security health of IT environments. They leverage extensive databases of known vulnerabilities and use various techniques, including port scanning and version checks, to detect security risks. By deploying and regularly using these scanners, organizations can patch vulnerabilities, fortify their defenses, and comply with regulatory requirements, minimizing the risk of cyber threats.

This is part of a series of articles about application security testing

In this article:

Key Features of Vulnerability Scanners 

Here are some of the key capabilities of modern vulnerability scanners:

1. Automated Discovery

Vulnerability scanners can identify every device on your network – be it servers, workstations, printers, or routers – and create an inventory of all your assets. This is the first step in securing your network; knowing what needs protection.

Automated discovery can provide insights into the makeup of your network, which can be highly dynamic, with new devices connecting and disconnecting. By maintaining an up-to-date inventory, you’re laying the groundwork for thorough security management.

Continuous discovery also ensures that no rogue or unauthorized device goes unnoticed. In the event a new, unfamiliar device appears on your network, the vulnerability scanner can identify it and enable you to take action.

2. Vulnerability Detection

Once the automated discovery has mapped out your network, the scanner can start detecting vulnerabilities. It meticulously examines each asset for known vulnerabilities, comparing your systems against databases of known security issues, such as the Common Vulnerabilities and Exposures (CVE). 

The detection process might look for misconfigurations, outdated software, missing patches, and other flaws that could be exploited. Different vulnerability scanners might address different types of vulnerabilities.

3. Risk Assessment

Next, vulnerability scanners prioritize the detected vulnerabilities based on the risk they pose to your organization. This assessment takes into account the severity of the vulnerability, the importance of the affected system, and the potential damage that could be caused if it were to be exploited. This prioritization allows you to focus your efforts on patching the most critical vulnerabilities first, ensuring the most effective use of your resources.

4. Reporting

Finally, vulnerability scanners generate detailed reports. These reports provide you with a clear view of your security posture, outlining the vulnerabilities detected, their risk levels, and recommendations for remediation.

These insights are invaluable for IT teams, executives, and even regulatory bodies that require proof of compliance with security standards. The analytics help track your progress over time, showing how your security posture has improved with each scan and remediation effort.

Types of Vulnerability Scanners 

Network Vulnerability Scanners

Network vulnerability scanners can inspect your entire network infrastructure – from servers and workstations to switches and firewalls – for vulnerabilities that could be exploited by attackers.

Network scanners can identify weak points in your network’s defenses, such as open ports, insecure network protocols, and services that should not be exposed to the public internet. These scanners are typically used as a first line of defense, providing a wide-angle view of your organization’s vulnerability landscape.

Web Application Vulnerability Scanners

Web application vulnerability scanners are crucial for identifying security weaknesses in websites and web applications. These scanners come in two main types: static application security testing (SAST) tools and dynamic application security testing (DAST) tools. 

SAST tools, or static scanners, analyze source code or compiled versions of code to identify vulnerabilities without executing the program. This approach allows developers to find and fix security issues early in the software development lifecycle. SAST tools are effective in detecting vulnerabilities related to code quality, such as cross-site scripting (XSS) and SQL injection, before the application is run.

DAST tools assess applications in their running state, mimicking an attacker’s approach to identify security flaws. This dynamic analysis is performed from the outside, scanning web applications for vulnerabilities without access to the source code. DAST tools are particularly useful for detecting runtime and environment-related vulnerabilities, such as authentication and session management issues, which are not visible until the application is running. 

Learn more about Bright Security’s Dev-Centric DAST

Container Vulnerability Scanners

With the rise of containerization technologies like Docker and Kubernetes, container vulnerability scanners have become increasingly important. These scanners specialize in finding vulnerabilities within container images and container management platforms.

Containers are a popular way to package and deploy applications, but they also introduce a new set of security challenges. If a container image has vulnerabilities, they can be propagated across numerous instances, leading to widespread security risks.

Container vulnerability scanners examine the layers within container images for known vulnerabilities and misconfigurations, ensuring that your containerized applications are not introducing risks into your environment.

Related content: Read the guide to container security

Cloud Vulnerability Scanners

Lastly, with the shift toward cloud computing, cloud vulnerability scanners have emerged to address the unique challenges of cloud environments. These scanners assess the security posture of your cloud infrastructure, including compute instances, storage, and network configurations.

Cloud environments are dynamic and scalable, which introduces complexities in maintaining a secure state. Cloud vulnerability scanners need to work hand-in-hand with cloud service provider APIs to provide visibility into the security of cloud resources.

How to Choose a Vulnerability Scanner Tool 

Assess the Complexity and Scale of your IT environment

The complexity and scale of your environment will significantly influence the type of vulnerability scanner you require. Start by cataloging the types of devices, systems, and applications within your ecosystem. Do you have a mix of operating systems? Are there any legacy systems or bespoke applications? How extensive is your web presence? Answering these questions will give you a blueprint of the necessary capabilities your vulnerability scanner must possess.

Furthermore, consider the pace at which your IT environment evolves. Fast-changing environments with frequent deployments may need scanners that can keep up with continuous integration/continuous deployment (CI/CD) pipelines and agile methodologies. In contrast, more stable environments might be well-served by scheduled scans.

Choose the Deployment Model

There are two common deployment models for vulnerability scanning solutions:

  • On-premises: An on-premises vulnerability scanner resides within your local infrastructure. This model offers you complete control over the scanning process and the data it generates.
  • Cloud-based: A cloud-based vulnerability scanner is operated by a service provider. This option can be more scalable and cost-effective, especially for businesses without the resources to manage and maintain on-premises software. Cloud scanners are also easier to update with the latest threat intelligence due to their centralized nature.

Your selection here will depend on factors such as regulatory compliance, data sensitivity, resource availability, and scalability requirements. In addition, if your infrastructure is primarily in the cloud, a cloud-based scanner might be a natural choice.

Consider the Scanner’s Accuracy

The precision with which a vulnerability scanner identifies and categorizes potential threats is a core consideration. False positives, where benign items are mistakenly flagged as threats, can waste valuable time and resources. Conversely, false negatives – actual vulnerabilities that go undetected – can leave your systems exposed to attacks.

Investigate the scanner’s track record for accuracy by seeking out reviews, case studies, and independent evaluations. These resources can provide insights into how well the scanner performs in real-world environments. You should also consider the scanner’s ability to adapt to new threats.

Ensure the Scanner Integrate with Existing Security and IT Tools

Integration is a crucial aspect of any vulnerability scanner. When a scanner integrates seamlessly with your tools, it can provide richer contextual insights, ease remediation, and even help automate responses to detected vulnerabilities.

Look for scanners that offer robust APIs or out-of-the-box integrations with widely used security information and event management (SIEM) systems, patch management tools, and other critical IT management solutions. This connectivity enables you to create a cohesive and responsive security infrastructure.

Learn more about Bright security’s dynamic vulnerability scanning