What Is CSRF Token Mismatch and 6 Ways to Fix It

Table of Content

  1. What Is CSRF?
  2. What Does CSRF Token Mismatch Mean? 
  3. Example of CSRF Token Mismatch: Laravel API
  4. 6 Ways to Solving the “CSRF Token Mismatch Error” 

What Is CSRF?

Cross-Site Request Forgery (CSRF) is a web application attack that forces an end user to execute unwanted actions on a web application in which they’re authenticated. CSRF attacks specifically target state-changing requests, not theft of data, since the attacker has no way to see the response to the forged request.

With a little bit of social engineering, such as sending a link via email or chat, an attacker may trick the users of a web application into executing actions of the attacker’s choosing. If the victim is a normal user, a successful CSRF attack can force the user to perform state changing requests like changing their email address or password. If the victim is an administrative account, CSRF can compromise the entire web application.

What Does CSRF Token Mismatch Mean? 

CSRF tokens are random, unique values associated with a user’s session. They are used to verify that requests and submissions made to a particular website originated from that site. The CSRF token mismatch error occurs when the CSRF token in a user’s session doesn’t match the one sent with their request.

Consider a user visiting a website which is protected against CSRF attacks by using CSRF tokens. Every time the user sends a request or submits data, the website checks that the CSRF token sent with your request matches the one associated with your session. If these tokens don’t match, it’s a CSRF token mismatch, and the website will return an error, potentially preventing the user’s request from going through. There are two possibilities:

  • The user is experiencing a CSRF attack: In this case, the CSRF token mismatch error can effectively block the attack.
  • The user is not experiencing a CSRF attack: This is the more common case, and this means the CSRF token mismatch error is a technical issue, which needs to be resolved to avoid hurting the user experience.

Related content: Read our guide to CSRF attack

Example of CSRF Token Mismatch: Laravel API

Laravel, a popular PHP framework for web application development, provides in-built CSRF protection. Laravel’s CSRF middleware automatically generates a CSRF token for each active user session managed by the application. This token is stored in the user’s session data and also embedded in HTML forms as a hidden field or added to the header of AJAX requests.

Laravel requires that every POST, PUT, PATCH, and DELETE request includes the CSRF token. It automatically checks this token against the one stored in the session. If they don’t match, Laravel throws a TokenMismatchException.

Here are the most common causes of a CSRF token mismatch error in Laravel:

  • Session timeout: If the user’s session expires due to inactivity, the CSRF token stored in the session is no longer valid. Any subsequent requests with the old CSRF token will result in a mismatch.
  • Form page caching: If a form page is cached, the CSRF token embedded in the form might be outdated by the time the user submits the form.
  • AJAX requests: For AJAX requests, if the CSRF token is not included in the request headers or is outdated, it will cause a mismatch.
  • Configuration issues: Incorrect configuration of session or middleware settings in Laravel can lead to improper handling of CSRF tokens.

And here are a few quick solutions:

  • Refreshing CSRF token: For session timeout issues, ensure that the CSRF token is refreshed when a new session is created. You can use the csrf_field() helper function in forms and include the CSRF token in AJAX request headers.
  • Disabling caching for forms: To prevent outdated CSRF tokens in cached forms, set appropriate cache-control headers to prevent caching of form pages.
  • Handling AJAX requests: Ensure that AJAX requests include the CSRF token in the request headers. This can be automated by setting a common header with the CSRF token for all AJAX requests in your JavaScript code.
  • Configuring sessions and middleware: Review Laravel’s session and middleware configurations to ensure they are set up correctly. Pay attention to session lifetime and the order of middleware in the kernel.php file.

6 Ways to Solving the “CSRF Token Mismatch Error” 

We cannot cover specific solutions to the CSRF token mismatch error in all possible web applications. However, here are a few general approaches that can help resolve the problem.

1: Check if the CSRF Tokens are Actually Mismatched

First thing, it is important to ensure that the CSRF tokens from the client and server are indeed mismatched. This verification can be done by logging both tokens and comparing them.

Remember, CSRF tokens are usually generated for each session or form, and they should be unique. When a form is submitted, the server compares the CSRF token sent with the request against the one stored in the session. If they do not match, you will encounter the CSRF token mismatch error.

In case the tokens are not mismatched, the problem may lie elsewhere. If they are, you’ve identified the problem and can proceed to one of the solutions below.

2. Clear Cookies from the Browser

Sometimes, the solution can be as simple as clearing cookies from the browser. Old or corrupted cookies can cause a CSRF token mismatch error.

To clear cookies, go to your browser settings and find the option to clear browsing data or cookies. Once the cookies are cleared, try to perform the action that was causing the error again.

Remember, while clearing cookies can solve the issue temporarily, it may not be a permanent fix if the problem lies elsewhere in your code or application setup.

3. Make Sure CSRF Tokens are Generated and Passed Correctly

After confirming a CSRF token mismatch, the next step is to make sure the tokens are generated and passed correctly. The generation of CSRF tokens is usually handled by your web framework. However, you need to ensure they are included in your forms or AJAX requests.

Check your form to ensure that it includes a CSRF token. If you’re using AJAX requests, make sure the CSRF token is included in the request header. This process is crucial because even if the server generates a CSRF token, it won’t be able to verify the request if the client doesn’t send one.

4. Check if the Session and CSRF Token Has Expired

Another common cause of a CSRF token mismatch is an expired session or CSRF token. Most web applications are designed such that CSRF tokens expire after a period of inactivity, which is a good practice for security reasons.

To check if this is the case, look at the expiration time of your sessions and CSRF tokens. If the user was inactive for longer than this period, their session or CSRF token may have expired.

If you find that tokens are expiring too quickly, causing inconvenience to your users, you may want to consider lengthening the expiration time. However, remember to strike a balance between user convenience and application security.

5. Check for JavaScript Errors in the Console

Sometimes, the issue could stem from a JavaScript error. If your application relies heavily on JavaScript, an error could prevent the CSRF token from being included in requests.

To check for JavaScript errors, open your browser’s console and look for any red error messages. Debug and fix any errors you find.

6. Consider Using Double Submit Cookies as an Additional Check

Double submit cookies present another layer of security. In this method, the server sends a CSRF token as a cookie alongside the regular CSRF token. When a request is made, the server checks both the CSRF token and the cookie values to detect a mismatch.

This approach can help identify a CSRF token mismatch error by providing an additional check. However, it should be used as an added layer of security and not a replacement for other necessary checks.

Application Mapping for Securing Business Applications

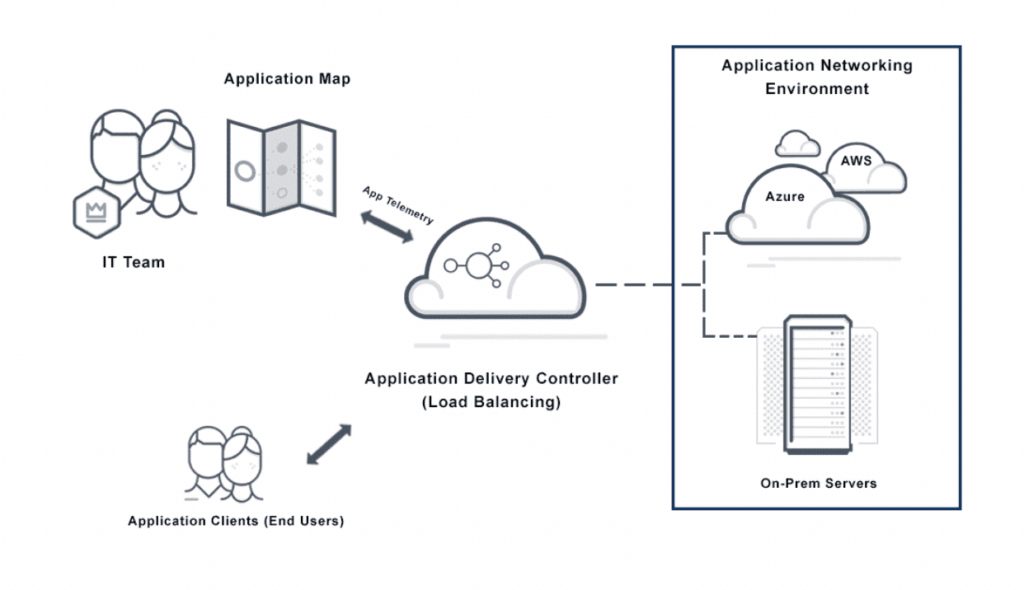
In the intricate web of modern business technologies, securing critical applications is paramount. Application mapping emerges as a vital tool in this context, offering numerous benefits for enhancing application security.

Application mapping, in the context of information technology and cybersecurity, refers to the process of creating a detailed inventory of an organization’s software applications and their interactions. This involves identifying and documenting various components of the applications, such as servers, databases, external services, and APIs, as well as understanding how they communicate and interconnect. 

Application mapping is crucial for organizations to comprehend their IT infrastructure’s complexity, manage dependencies, ensure efficient performance, and identify potential security vulnerabilities within their application ecosystem. This comprehensive understanding aids in effective IT management, strategic planning, and bolstering security measures against potential threats.

Let’s delve into the five key security advantages that application mapping provides.

1. Enhanced Visibility and Control

Application mapping offers a comprehensive view of an organization’s application landscape. By delineating how applications interact, the data they utilize, and their interdependencies, organizations gain critical insights. This enhanced visibility is not just operationally beneficial but pivotal for security. It enables the identification of potential security vulnerabilities within the application ecosystem, allowing organizations to take proactive steps to address them. Moreover, with greater control over the application environment, organizations can manage their applications more effectively and securely, ensuring a fortified defense against potential threats.

2. Improved Compliance and Risk Management

In today’s regulatory landscape, adherence to industry-specific standards is a major concern for businesses. Non-compliance can lead to significant financial penalties and reputational harm. Application mapping can be a powerful ally in ensuring compliance. By providing a detailed overview of the application landscape, it highlights areas that may not align with current security standards or regulations, such as applications using outdated protocols. This facilitates timely remediation to maintain compliance.

Risk management also benefits from application mapping. Understanding the application ecosystem in its entirety allows for a more accurate assessment of potential risks and the development of targeted mitigation strategies, enhancing the organization’s overall security posture.

3. Efficient Incident Response and Recovery

In the event of a security breach, rapid response is crucial to minimize damage. Application mapping significantly enhances an organization’s ability to respond to and recover from security incidents. With a clear map of the application ecosystem, affected applications and their dependencies can be swiftly identified, isolating the breach and preventing further system infiltration. This knowledge is invaluable in guiding recovery efforts, ensuring applications are restored systematically to reduce downtime and operational impact.

4. Identifying Anomalies and Potential Threats

Early detection of anomalies and threats is critical in preventing security breaches. Application mapping aids in establishing a baseline for normal application behavior and interactions. Deviations from this baseline can signal potential security issues. For example, unexpected communication between an application and an external server might indicate a compromise. A detailed application map is instrumental in detecting such anomalies, enabling quick and effective responses to emerging threats.

5. Data Protection and Privacy Enhancement

In an era where data breaches are rampant and data protection regulations are stringent, safeguarding data privacy is more crucial than ever. Application mapping enhances an organization’s ability to protect data. By tracing data flow within the application ecosystem, organizations gain clarity on data storage, usage, and access. This aids in pinpointing potential data leakage points and implementing necessary security measures. Additionally, understanding data flow is essential for compliance with regulations like the GDPR, helping organizations avoid hefty fines and reputational damage.

Implementing Application Mapping

Here’s a comprehensive guide on how to successfully implement application mapping in an organization:

Setting Clear Objectives and Establishing Scope: 

  1. Defining Goals: Begin by pinpointing what you aim to achieve through application mapping. This could range from enhancing application performance, minimizing downtime, to streamlining IT operations.
  2. Determining the Scope: Identify the applications to include in your mapping. Will it be limited to critical applications or encompass the entire suite across your organization? This decision hinges on your defined goals and available resources, and it’s crucial for guiding the subsequent steps of the process.

Comprehensive Inventory of Current Applications: 

  1. Cataloging Your Applications: Create an exhaustive inventory of all applications in use. Detail each application’s purpose, user base, and dependencies. This step is pivotal in offering a transparent view of your current application ecosystem, laying the groundwork for identifying areas of improvement and potential integration challenges.

Mapping Inter-Application Dependencies: 

  1. Understanding Interactions: With your inventory at hand, the next phase is to untangle and map out how each application interacts within your network. Leveraging application mapping tools can automate and streamline this process.
  2. Revealing Complexity: This step uncovers the intricacies of your application network. It helps in comprehending how alterations in one application might ripple through others, aiding in more efficient management and reducing risks associated with changes.

Visual Representation of Your Application Landscape

  1. Creating a Visual Blueprint: Transform your data into a visual map of your application network. This visualization should capture the network’s structure at various levels, providing insights into its complexity and interconnectivity.
  2. Insights and Overview: This visual guide is not just a technical asset but a communication tool. It highlights potential bottlenecks and vulnerabilities, flags optimization opportunities, and offers stakeholders an accessible overview of your IT ecosystem.

Conclusion

As the reliance on applications continues to escalate in the business world, recognizing and addressing their security vulnerabilities becomes a non-negotiable aspect of organizational strategy. Application mapping offers an in-depth analysis of the risks inherent in application ecosystems and provides actionable strategies to strengthen their security frameworks. It’s not merely about mitigating risks; it’s about reshaping the security paradigm to align with the evolving digital environment. By prioritizing application mapping, businesses can significantly lower the threat landscape and ensure that their applications are not just operational but also secure and compliant. In a landscape where digital agility is intertwined with security, application mapping is not just a tool – it’s an imperative.

Penetration Testing Tools: 10 Tools to Supercharge Your Pentests

Table of Content

  1. What are Penetration Testing Tools?
  2. Penetration Test Phases
  3. Types of Penetration Testing Tools
  4. Top 10 Pentesting Tools
  5. Penetration Testing with Bright

What are Penetration Testing Tools?

Penetration testing (pentesting) is a simulated attack launched for the purpose of uncovering security vulnerabilities. A pentest helps organizations discover security gaps, using a realistic simulation of a cyber attack, which does not cause damage or expose sensitive data. There are several tools available for this purpose:

  • Bright Security is an advanced penetration testing tool based on the dynamic application security testing (DAST) approach, which uses artificial intelligence to identify complex security vulnerabilities traditional methods might miss. 
  • Metasploit can perform vulnerability scanning, listening, and evidence collection, making it a good choice for pentesters who manage multiple companies or applications.
  • Kali Linux is a pentesting operating system including multiple powerful tools, including sniffing and injecting, password cracking, and digital forensics.
  • Burp Suite offers both a free community edition and a commercial professional edition, and is a versatile web application security testing tool. 
  • Nmap is capable of scanning a single IP, port, or host to a range of IPs, ports, and hosts, and can also identify services that are running on hosts. 
  • Sqlmap, with its testing engine and multiple modes of injection attacks, is good for detecting injection flaws, but may be limited in detecting other vulnerabilities. 
  • Wireshark, an open-source tool, analyzes network traffic in real-time and can show which systems and protocols are live in a network.
  • Zed Attack Proxy (ZAP) is a free and libre software that sits between your browser and the website you’re testing.
  • Nessus can examine a target machine, identify running services, and provide a list of detected vulnerabilities. 
  • Aircrack-ng is designed specifically for cracking flaws within wireless connections.
  • Nikto, an open source web server scanner, performs comprehensive tests against web servers. 

Other notable penetration testing tools include Cain and Abel, CANVAS by Immunity, John the Ripper, Kali Linux, Struts-Scan, and W3af.

Related content: read our guide to penetration testing services

In this article, you will learn:

Penetration Test Phases

The penetration testing process usually occurs in five stages. In each of these stages, penetration testers use tools to automate data gathering and exploitation of organizational resources.

  1. Planning and reconnaissance—the pentester defines the goal and scope of the test. To properly plan the test, the pentester gathers intelligence, which can help in better understanding how a targeted environment works and discover its potential weaknesses.
  2. Scanning—helps the pentester to better understand how the targeted application might respond to various intrusion attempts. The pentester may use either static or dynamic analysis to access a network.
  3. Gaining access—the pentester uses several pentesting techniques, such as SQL injection and cross-site scripting (XSS), to detect vulnerabilities.
  4. Maintaining access—the pentester tries to understand if a cybercriminal can exploit weakness, achieve persistent presence in the system, and gain more access.
  5. Analysis—the pentester compiles the results of the penetration test into a detailed report. The report usually specifies the vulnerabilities that were exploited, the time spent undetected within the system, the sensitive data that was accessed, and more.

Types of Penetration Testing Tools

There is a wide range of tools you can use when running a pentest, each providing different capabilities. Here are the most commonly used penetration testing tools:

  • Port scanners—can locate potential attack vectors during the reconnaissance phase. A port scanner can detect open ports, which provide insight into operating systems (OS) and applications running with network access. 
  • Vulnerability scanners—can identify known application vulnerabilities and configuration errors. A pentester can use the report generated by a vulnerability scanner to identify an exploitable vulnerability for initial access. 
  • Network sniffers—can collect and analyze network traffic. A pentester can use a network sniffer to locate active applications and then look for sensitive data or exposed credentials moving through the network.
  • Web proxy—can help pentesters intercept and change traffic flowing between the pentester’s browser and the web server of the organization. The goal is to find and exploit HTML application vulnerabilities, which enable the tester to launch attacks like XSS and cross site request forgery (CSRF).
  • Password cracker—can help pentesters identify weak passwords within the network. Attackers use password hashes to expand or elevate their privileges levels. A password cracker helps pentesters determine if weak passwords are putting the network at risk.

Related content: read our guide to web application penetration testing

Top 10 Pentesting Tools

Here are ten of the best and most commonly used tools used in penetration tests.

Bright Security

Bright provides a penetration testing platform powered by artificial intelligence (AI). It lets organizations automate and scale the detection of vulnerabilities, including zero-day attacks, business logic weaknesses, and known vulnerabilities.  

Bright automatically scans multiple layers of your environment and provides comprehensive reports, guaranteed to be free of false positives, on par with reports provided by manual penetration testers.

Metasploit

Metasploit is a popular open source framework for penetration testing. The tool lets you pass a code that breaches a system, and then runs a payload that performs actions on a target machine. Metasploit is often used for manual brute force attacks and website pentesting.

You can use Metasploit on various environments, including servers, applications, and networks. It comes with a clickable graphical user interface (GUI), which works on Linux, Microsoft Windows, and Apple Mac OS.

Burp Suite

Burp Suite is a comprehensive web vulnerability scanner, which supports both automated and manual testing of web applications. It includes tools for mapping out application contents, analyzing requests and responses, and identifying security flaws. 

The professional edition offers features like automated scanning, intruder attacks, and the ability to save and resume sessions. Its user-friendly interface and powerful testing capabilities make it a favorite among security professionals.

Kali Linux

Kali lets you configure customized backup and recovery schedules, but it works only on Linux. Kali offers the use of several tools, curated to help you perform many penetration testing tasks, including sniffing and injecting, password cracking, and digital forensics. Kali is offered under the open source license, and can be integrated with Metasploit and Wireshark.

Nmap

Nmap (Network Mapper) is a free and open-source utility for network discovery and security auditing. It is used to discover hosts and services on a computer network by sending packets and analyzing the responses. 

Nmap provides a variety of features for probing computer networks, including host discovery, port scanning, version detection, and OS detection. It is a versatile tool that can be used for a range of network-related tasks, from inventorying the network to monitoring host or service uptime to network security auditing.

Sqlmap

Sqlmap is an open source tool that provides automation capabilities for detecting and exploiting SQL injection vulnerabilities. The tool provides password cracking capabilities, and lets you execute arbitrary code commands. It supports six SQL injection techniques and lets you directly connect to a database without having to pass through the injection. 

WireShark 

Wireshark is a network packet analyzer that captures live traffic and enables offline analysis. It supports most operating systems including Linux, Windows, Solaris, and FreeBSD. It provides both a graphical user interface and terminal interface. 

WireShark can analyze VoIP traffic, read live data from protocols like PPP/DLC, bluetooth and ATM, decompress compress files on the fly, and decrypt transmission encrypted by protocols like IPSec and WPA/WPA2.

Zed Attack Proxy (ZAP)

ZAP is an open source vulnerability scanner for web applications. It can perform passive scanning, or simulate attacks on applications to discover security weaknesses. ZAP can identify open ports, perform brute force search on files or directories, crawl to discover the structure of a site, and supply random inputs (fuzzing) to test if the website crashes or behaves unexpectedly.

Nessus

Nessus is one of the most widely used vulnerability scanning tools in the cybersecurity field. Developed by Tenable Network Security, it is known for its robust detection of vulnerabilities and misconfigurations in networks and systems. 

Nessus scans for known vulnerabilities, misconfigurations, and provides detailed remediation reports. Its continuously updated vulnerability database makes it effective in identifying the latest threats and compliance issues.

Aircrack-ng

Aircrack-ng is a suite of tools for assessing WiFi network security. It focuses on different areas of WiFi security: monitoring, attacking, testing, and cracking. With its ability to capture network packets and analyze them, Aircrack-ng can be used to recover lost keys of Wi-Fi networks, assess their security, and understand the strategies used by attackers to breach wireless networks.

Nikto

Nikto is an open-source web server scanner which performs comprehensive tests against web servers for multiple items, including over 6700 potentially dangerous files/programs, checks for outdated versions of over 1250 servers, and version-specific problems on over 270 servers. It also checks for server configuration items such as the presence of multiple index files and HTTP server options, and will attempt to identify installed web servers and software.

Penetration Testing with Bright

Bright goes far beyond finding the OWASP Top 10 technical vulnerabilities in your applications and APIs. With more than 7,000 payloads Bright’s AI powered engine automatically detects a long list of known vulnerabilities and unknown Zero-Day and Business-Logic Flow vulnerabilities. 

This significantly reduces lengthy and costly manual testing, saving you time and money with False Positive free reporting and remediation guidelines. Bright is also built for automation. It seamlessly integrates into your SDLCand provides false-Positive Free reports generated in real-time, with pinpoint code instrumentation, empowering the highest security standards, without losing development speed or agility.

Learn more about Bright

An Introduction to Software Supply Chain Attacks

Table of Content

  1. What is the Software Supply Chain?
  2. What is a Software Supply Chain Attack? 
  3. What Are the Types of Attacks?
  4. What Can Be Done to Prevent Attacks?
  5. Summary 

The alarming rise in Software Supply Chain (SSC) attacks has catapulted this issue into a hot topic in the cybersecurity landscape. A staggering 742% increase in these attacks over the past three years, as reported by CSO Magazine, underscores the urgency for organizations to address this escalating threat. SSC attacks continue to be newsworthy with notable examples of software supply chain attacks including SolarWinds, Home Depot, and NotPetya incidents.

In response to this heightened risk, businesses are redoubling their efforts to implement robust safeguards against SSC attacks. Concurrently, leading industry organizations are continually releasing targeted guidance aimed at assisting enterprises in fortifying their software supply chains against potential breaches.

What is the Software Supply Chain?

To fully grasp the nature of a supply chain attack, it is important to understand the contemporary landscape of application development. Gone are the days when applications were monolithic entities, crafted entirely in-house from the ground up. Modern application development is more akin to assembling a complex mosaic, where each piece—a library here, a framework there, complemented by various web services and databases—comes together to form a functional and efficient whole.

This modular approach allows developers to accelerate the development cycle, reusing code that has been proven effective, and focusing their efforts on innovating rather than reinventing the wheel. However, this interconnectedness also brings to light a new set of complexities. Each component integrated into an application may itself be constructed from other subcomponents, creating a nested hierarchy of dependencies.

Take the widely used Log4J logging library within the Apache framework as a case in point. When a critical vulnerability within Log4J was uncovered, it cascaded through the ecosystem, impacting any and all applications that relied on it, illustrating just how pervasive and profound the effects of a single weakness can be.

The modern, layered approach to building applications enables rapid development and innovation. Yet, it simultaneously introduces a systemic risk: if any single component in the network of dependencies is compromised, the entire structure can be at risk, making it imperative for developers to diligently manage and monitor these interdependencies.

What is a Software Supply Chain Attack? 

Supply chain attacks strategically focus on infiltrating an organization by compromising the products, in this case the software that the targeted entities depend on. In this type of cyber-assault, attackers covertly implant a backdoor within the software or its development infrastructure. Once established, this concealed entry point grants them the ability to tamper with the software’s update and patching mechanisms. They exploit this capability to deliver “trojanized” updates—updates that appear legitimate but are laced with malicious code. 

When the unsuspecting organization applies these tainted updates, they unknowingly open the floodgates for an array of cyber threats. This can include sophisticated malware intrusions, ransomware attacks, and even advanced persistent threats (APTs) that lurk stealthily within the network, gathering intelligence or waiting for an opportune moment to strike. 

The insidious nature of software supply chain attacks makes them particularly dangerous, as they abuse the inherent trust organizations place in their software suppliers and the updates they provide. This makes it all the more imperative for organizations to diligently scrutinize their software supply chain for potential vulnerabilities.

Historically, supply chain attacks have referred to attacks against trusted relationships, in which an unsecure supplier in a chain is attacked in order to gain access to their larger trading partners. This is what happened in the notorious 2013 attack against Target, where the threat actor gained access to an HVAC contractor in order to enter Target’s systems.

What Are the Types of Attacks?

Software supply chain threats include, but are not limited to:

  • Malicious code injection: Insert malicious code into the software during the development or distribution stage leading to serious security breaches and data theft.
  • Tampering with updates: Attackers can modify software updates to include malicious code compromising the security of the software and leading to data theft.
  • Unauthorized access to the code repository: Attackers can gain access to the code repository and make changes to the software code, leading to security vulnerabilities.
  • Compromised third-party libraries: An attacker may gain access to the code repository and make changes to the software code.

What Can Be Done to Prevent Attacks?

Preventing supply chain security attacks involves implementing various security measures throughout the software development lifecycle, from design to deployment and upgrades. Here are some steps that can be taken to prevent attacks on your software supply chain:

  • Establish security policies and standards: Access control, authentication, data validation assessment, and protection.
  • Verify the integrity of software: Digital signatures, checksums, or other methods.
  • Secure build environment: Secure build system access, secure software repositories, scan-build artifacts, and images for vulnerabilities.
  • Run security assessments: Analysis to identify vulnerabilities and weaknesses in the software, including static and dynamic code analysis and vulnerability scanning.
  • Use trusted sources: Use trusted sources for software and components, such as official repositories, verified vendors, and licensed and verified versions.
  • Implement security controls: Use firewalls, intrusion detection systems, and access controls to protect against attacks.
  • Monitor and respond to security incidents: Monitor vulnerabilities and security incidents and respond quickly to any incidents to minimize the impact.
  • Foster a security culture: Easy-to-use tools for training employees on secure coding practices, password management, content analysis, and incident response.

Summary 

Defending against software supply chain attacks is of paramount importance due to their ability to stealthily compromise widespread systems through a single point of vulnerability. As software increasingly relies on a complex network of third-party components and services, the risk surface expands, making it crucial to ensure that each element within the supply chain is secure. These attacks can lead to significant data breaches, operational disruptions, and loss of customer trust, affecting not just individual organizations but also the broader ecosystem that relies on the integrity of the software supply chain. 

Effective defense against these threats requires rigorous security practices, including thorough vetting of third-party components, continuous monitoring for anomalies, and swift incident response protocols. By safeguarding the supply chain, organizations can protect their assets, maintain compliance with regulations, and uphold their reputations in an increasingly interconnected digital landscape.

Data Breaches: Causes, Compliance Impact, and Best Practices

Table of Content

  1. What Is a Data Breach? 
  2. Consequences of a Data Breach 
  3. 4 Causes of Data Breaches
  4. Data Breach Requirements in Common Compliance Standards 
  5. Best Practices to Prevent Data Breaches 
  6. See Additional Guides on Key Information Security Topics

What Is a Data Breach? 

A data breach is an incident where unauthorized individuals gain access to confidential data stored in a system. This data can include personal information such as credit card numbers, social security numbers, or corporate information like trade secrets and intellectual property.

Some data breaches are orchestrated by cybercriminals intending to exploit the data for malicious purposes. This could involve selling the data on the dark web, holding it ransom, or using it for identity theft. However not all data breaches are carried out by hackers. For example, some occur due to human error or insider threats.

In essence, a data breach represents a violation of trust and security. It can disrupt an organization’s operations, irreparably hurt its reputation, and in regulated industries, can result in compliance violations and legal problems. This is why every organization must have a strategy for preventing and mitigating data breaches.

This is part of a series of articles about information security.

In this article:

Consequences of a Data Breach 

The consequences of a data breach can be far-reaching, affecting not just businesses but also individuals and society at large:

Financial Implications for Businesses

A data breach can have severe financial implications for businesses. These include the immediate costs associated with the breach’s detection and containment, investigation, and recovery. However, the financial repercussions of a data breach extend beyond these immediate costs.

Businesses might also face financial losses due to business disruption and lost sales. Moreover, there is the looming threat of lost business opportunities and contracts due to damaged trust and reputation. In some cases, businesses may also need to compensate affected customers, adding to the overall financial burden.

Data breaches can also result in legal and regulatory penalties. Depending on the jurisdiction and the nature of the data compromised, companies may face hefty fines and sanctions. For instance, under the General Data Protection Regulation (GDPR) in the European Union, businesses can be fined up to 4% of their annual global turnover for serious data breaches.

Moreover, companies may also face lawsuits from affected customers or employees. These legal battles not only result in financial losses but also consume valuable time and resources that could otherwise be invested in productive activities.

Learn more in our detailed guide to security breach.

Reputational Damage and Loss of Customer Trust

Perhaps the most devastating consequence of a data breach is the damage it does to a company’s reputation. Customer trust is a crucial business asset, and a data breach can erode this trust.

Customers entrust businesses with their personal and financial information, expecting that it will be kept safe. A data breach shatters this expectation, leading to a loss of customer trust. This can result in customers turning to competitors, leading to a decline in customer base and revenue.

Personal and Societal Impacts

Beyond businesses, data breaches also have significant personal and societal impacts. Individuals affected by a data breach may fall victim to identity theft, financial fraud, and other forms of cybercrime. This can lead to emotional distress, financial losses, and violation of privacy.

At a societal level, data breaches can undermine trust in digital platforms and systems. This could potentially hamper the adoption of digital services, slowing down the pace of digital transformation. Moreover, large-scale data breaches can even pose a threat to national security.

4 Causes of Data Breaches

There are four main ways in which data breaches can occur:

1. Cyberattacks

Cyberattacks are a common means by which data breaches occur. Hackers employ a variety of techniques to gain unauthorized access to data. These include phishing attacks, malware, ransomware, and denial of service attacks. These attacks exploit various weaknesses in a system’s security to steal, damage, or disrupt access to data.

2. Insider Threats

Insider threats refer to data breaches that occur due to the actions of an individual within an organization. This could be a disgruntled employee, a careless staff member, or even a malicious insider working for a competitor or a cybercriminal group. Insider threats can be particularly challenging to detect and prevent, given the level of access and trust these individuals often have.

3. Human Error

Human error is another significant cause of data breaches. This could involve employees accidentally sending sensitive information to the wrong recipient, leaving systems unsecured, or falling for phishing scams. Despite being unintentional, the impact of such breaches can be just as severe.

4. System Vulnerabilities

Lastly, system vulnerabilities often serve as a gateway for data breaches. These vulnerabilities could be due to outdated software, weak passwords, or lack of proper security measures. Hackers often exploit these weaknesses to gain access to a system and the data stored within.

Data Breach Requirements in Common Compliance Standards 

General Data Protection Regulation (GDPR)

The GDPR is a European Union regulation that provides individuals with more control over their personal data. It requires organizations to protect the privacy and integrity of data they hold about EU citizens, regardless of where the company is located.

Under the GDPR, organizations are required to report a data breach to the appropriate supervisory authority within 72 hours of becoming aware of it. They must also notify affected individuals without undue delay if the breach poses a high risk to their rights and freedoms. The notification should describe the nature of the breach, the likely consequences, and the measures taken to mitigate its possible adverse effects.

The GDPR imposes significant penalties for non-compliance. Organizations can face fines of up to 20 million Euros or 4% of their global annual revenue, whichever is higher, if they fail to comply with the regulation’s requirements. In addition, they may suffer reputational damage, legal action, and loss of consumer trust.

California Consumer Privacy Act (CCPA)

The CCPA is a state statute intended to enhance privacy rights and consumer protection for residents of California. Although it has a narrower scope than the GDPR, the CCPA has substantial implications for businesses that collect, store, and process personal information of California residents.

Under the CCPA, businesses are required to disclose their data collection practices and allow consumers to opt-out of the sale of their personal information. In case of a data breach, businesses have to notify affected consumers without unreasonable delay. The notification must include details about the breach, types of information compromised, and steps consumers can take to protect themselves.

Non-compliance with the CCPA can result in penalties of up to $7,500 per violation, not to mention potential lawsuits from affected consumers. Therefore, businesses need to ensure they have robust data security measures in place to prevent data breaches and comply with the CCPA requirements.

PCI DSS

The PCI DSS is a set of security standards designed to secure credit and debit card transactions against data theft and fraud. It applies to all entities that store, process, or transmit cardholder data.

The PCI DSS requires businesses to build and maintain a secure network, protect cardholder data, maintain a vulnerability management program, implement strong access control measures, regularly monitor and test networks, and maintain an information security policy. In the event of a data breach, businesses must immediately contain and limit the exposure of cardholder data. They also need to alert all necessary parties, including their acquiring bank, card brands, and a PCI Forensic Investigator.

Failure to comply with the PCI DSS can result in penalties ranging from $5,000 to $100,000 per month. Moreover, businesses may lose their ability to process card payments, face increased transaction fees, and suffer reputational damage.

Health Insurance Portability and Accountability Act (HIPAA)

HIPAA is a federal law that protects sensitive patient health information from being disclosed without the patient’s consent or knowledge. It applies to healthcare providers, health plans, healthcare clearinghouses, and business associates of these entities.

Under HIPAA, covered entities and their business associates must implement administrative, physical, and technical safeguards to ensure the confidentiality, integrity, and availability of protected health information. In case of a data breach, they must notify affected individuals, the Secretary of Health and Human Services, and in some cases, the media, within 60 days. The notification must include a brief description of the breach, the types of information involved, the steps individuals should take to protect themselves, and what the covered entity is doing to investigate the breach, mitigate harm, and prevent further breaches.

Non-compliance with HIPAA can result in civil penalties of up to $1.5 million per violation category, per year. Criminal penalties can go up to $250,000 in fines and ten years in prison. In addition, covered entities may suffer reputational damage and loss of patient trust.

Best Practices to Prevent Data Breaches 

Conduct Regular Risk Assessments

Regular risk assessments are crucial in identifying your organization’s vulnerabilities and taking corrective actions before a breach occurs. This involves identifying and categorizing assets, evaluating potential threats, assessing vulnerability, analyzing controls, and quantifying the potential impact.

Risk assessments should be conducted at least annually or whenever significant changes occur in the business environment, such as after a merger or acquisition, when launching a new product, or when adopting new technologies.

Use Strong Authentication Methods

Strong authentication methods, such as two-factor authentication (2FA) or multi-factor authentication (MFA), can provide an additional layer of security. These methods require users to verify their identity by providing two or more pieces of evidence or credentials.

Implementing a robust password policy is equally important. This includes using unique passwords, changing them regularly, and using password managers to store them securely.

Encrypt Sensitive Data

Encryption is the process of converting data into a code to prevent unauthorized access. Sensitive data such as customer information, payment details, and internal documents should be encrypted both when stored (at-rest encryption) and when transmitted over a network (in-transit encryption). Using strong encryption algorithms and keeping encryption keys secure are vital components of this security measure.

Regularly Backup Data

Regular backups can help you recover your data in case of a breach or other forms of data loss. It’s crucial to backup data regularly and test the backups to ensure they work correctly.

You should store backups in a secure, off-site location and encrypt them to protect against unauthorized access. It’s also a good idea to keep multiple versions of backups in case one is corrupted or compromised.

Secure Physical Access

While much of data security focuses on digital threats, physical security is just as important. This involves restricting access to servers, data centers, and other areas where sensitive data is stored.

Physical security measures can include locks, biometric access controls, surveillance cameras, and security personnel. It’s also crucial to log and monitor physical access to detect and respond to any unauthorized access promptly.

Educate Employees

Employees are often the weakest link in an organization’s security chain. Therefore, it’s imperative to educate them about the importance of data security and the role they play in preventing data breaches.

This includes training them on best practices such as recognizing and reporting phishing attempts, using strong passwords, and following proper procedures when handling sensitive data. Regular training updates are also necessary to keep up with the evolving threat landscape.

Secure Applications and Databases

Software that handles and stores data should be built with security in mind. This includes securing databases through firewall rules, data masking, and access controls that limit who can view or modify the data. For applications, secure coding practices should be followed to prevent vulnerabilities that can be exploited, such as SQL injection or Cross-Site Scripting (XSS). Regular security audits and code reviews are necessary to identify and fix vulnerabilities.

See Additional Guides on Key Information Security Topics

Together with our content partners, we have authored in-depth guides on several other topics that can also be useful as you explore the world of information security.

SOAR

Authored by Exabeam

Bot Protection

Authored by Radware

Application Security

Authored by Oligo

Using SAST and DAST Integration for Reducing Alert Fatigue

Table of Content

  1. Understanding SAST and DAST
  2. The Synergistic Integration
  3. Tackling Alert Fatigue
  4. Conclusion

In the ever-evolving world of cybersecurity, there’s a relentless push to stay ahead of potential threats. For development teams and cybersecurity professionals, two methodologies have emerged as leaders in the realm of application security in pre-production: Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST). Each offers its own unique advantages, but when integrated, adopting a layered approach, they form a potent defense mechanism against vulnerabilities. Even more crucially, their combined strength can significantly reduce alert fatigue and assist AppSec and developer teams align priorities around these alerts based on risk and likelihood of specific attack vectors.

Understanding SAST and DAST

Before diving into the benefits of their integration, let’s briefly explore what each of these methods entails:

– SAST: Often referred to as “white box security testing”, SAST involves examining the application’s source code, bytecode, or binary code for vulnerabilities without executing the program. It can identify potential  vulnerabilities early in the development lifecycle, making it easier and less costly to fix. SAST identifies potential open attack vectors in the code, but the why the application is deployed can differ between real vulnerabilities to issues that are not really applicable as attack vectores when the application is deployed., 

– DAST: Dubbed “black box security testing”, DAST analyzes running applications, usually from an outsider’s perspective. It simulates how an attacker might exploit potential vulnerabilities in a live environment, without any prior knowledge of the internal workings of the application.

The Synergistic Integration

When you combine the introspective scrutiny of SAST with the external probing capabilities of DAST, the result is a holistic and layered approach to application security. Here’s why this union is groundbreaking:

1. Comprehensive Coverage: While SAST can identify potential vulnerabilities in the codebase, DAST can catch runtime vulnerabilities and issues stemming from the application’s environment or configuration. This dual approach ensures that both the application’s code and its behavior in a live setting are thoroughly vetted. DAST can simulate real-world attacks to check if vulnerabilities identified by SAST are genuinely exploitable. This gives a practical dimension to the theoretical findings of SAST.

2. Efficient Remediation: SAST provides detailed information about exactly where the vulnerability exists in the codebase, while DAST verifies and offers insights into how that vulnerability might be exploited. With this combined knowledge, developers can prioritize and address the most critical threats first, ensuring resources are utilized effectively.

3. Continuous Security: Both SAST and DAST can be integrated into the Continuous Integration/Continuous Deployment (CI/CD) pipeline. This means security checks can be automated and performed frequently, ensuring that vulnerabilities are detected and addressed as soon as they emerge.

Tackling Alert Fatigue

Alert fatigue occurs when security professionals are inundated with a multitude of alerts, many of which may be false positives or alerts of low priority. This constant barrage can lead to desensitization, causing teams to overlook or dismiss critical alerts. Given the high stakes in cybersecurity, this is a risk organizations cannot afford. So, how does the integration of SAST and DAST help?

1. Reduced False Positives: By corroborating findings from both methods, there’s a higher likelihood that the vulnerabilities identified are genuine. For instance, a vulnerability detected by SAST can be confirmed by DAST in a runtime environment, ensuring it’s not just a theoretical risk but a tangible one.

2. Prioritization of Alerts: With insights from both static and dynamic testing, security teams can differentiate between minor issues and critical vulnerabilities that need immediate attention. This helps in streamlining alerts and ensuring teams focus on what truly matters.

3. Streamlined Workflow: An integrated approach means there’s a single dashboard or interface where vulnerabilities from both SAST and DAST are presented. This consolidation reduces the cognitive load on security professionals, allowing them to process and act on alerts more efficiently.

Conclusion

4. Efficient Remediation: With insights from both static and dynamic testing, developers can pinpoint the exact location of vulnerabilities in the codebase and understand their real-world impact. This makes the remediation process faster and more effective.

In the complex landscape of application security, relying on a single method to detect vulnerabilities is no longer sufficient. By harnessing the strengths of both SAST and DAST, organizations can not only bolster their defenses but also create a more manageable and focused alert system.

Remember, it’s not just about finding vulnerabilities; it’s about understanding their potential impact, prioritizing them, and addressing them effectively. By integrating SAST and DAST, businesses can achieve just that, all while ensuring their security teams remain vigilant, responsive, and not overwhelmed by a sea of alerts.

In conclusion, when SAST and DAST are used together, they provide a holistic view of both the internal and external security vulnerabilities of an application, ensuring that it’s secured against potential threats. This combined approach enhances the depth and breadth of security testing, making applications more resilient to cyber threats.

Black Box Testing: Types, Techniques, Pros and Cons

Table of Content

  1. What Is Black Box Testing in Software Engineering? 
  2. Black Box vs. White Box Testing 
  3. Types Of Black Box Testing 
  4. Black Box Functional Testing Techniques 
  5. Common Black Box Security Testing Techniques 
  6. Black Box Functional Testing: Pros and Cons 
  7. Black Box Security Testing: Pros and Cons 
  8. When to Choose Black Box Testing in Your QA Strategy
  9. Black Box Testing Metrics and How to Measure Effectiveness
  10. How Black Box Testing Supports Security Validation
  11. Challenges Teams Face When Applying Black Box Testing
  12. Best Practices for Effective Black Box Testing 

What Is Black Box Testing in Software Engineering? 

Black box testing involves evaluating the functionality of software without peering into its internal structures or workings. The term “black box” refers to a system where the internal mechanics are unknown, and testing solely focused on the output generated by a given input.

When conducting black box testing, the tester doesn’t need knowledge of the internal structure of the software; the test is conducted from a user’s perspective. This type of testing can be applied to every level of software testing, including unit testing, integration testing, acceptance testing, and security testing.

The primary advantage of black box testing lies in its focus on the user perspective, ensuring that the software meets user requirements and expectations, and cannot be attacked by external malicious parties. It is not concerned with code efficiency or structure, but rather with functionality and usability, which are paramount for the end user.

This is part of a series of a series of articles about application security testing

Black Box vs. White Box Testing 

While black box testing focuses on the functionality without considering the internal structure of the software, white box testing involves the detailed investigation of internal logic and structure of the code.

White box testing is also referred to as “glass box”, “clear box”, or “structural testing”. It requires intricate knowledge of the internal workings of the code being tested. The tester is aware of the internal software structure and designs test cases to cover multiple paths through the software.

The primary difference between the two lies in their approach. While black box testing is input-output driven, white box testing is code driven. Both play a crucial role in software testing and are usually used in conjunction to create robust, reliable software.

Types Of Black Box Testing 

Here are the main types of black box testing:

Functional Testing

Functional testing is a type of black box testing that focuses on validating the software against functional requirements and specifications. It ensures that the software behaves as expected in response to specific inputs. Functional testing is conducted at all levels and includes techniques like unit testing, integration testing, system testing, and acceptance testing.

Non-Functional Testing

While functional testing focuses on what the software does, non-functional testing is concerned with how the software performs. It evaluates aspects like the performance, usability, reliability, and compatibility. Black-box non-functional testing checks these criteria from the end-user’s perspective. For example, a black-box performance test of a website might simulate a user session and measure the actual page load time.

Security Testing

Security testing is a type of black box testing that checks the software for any potential vulnerabilities or security risks. It aims to ensure that the software is secure from any threats and that the data and resources of the system are protected from breaches.

Black-box security testing is performed from the perspective of an external attacker, and can help identify vulnerabilities like injection attacks, denial of service attacks, and other security threats. It ensures that the software is robust enough to prevent and mitigate potential attack vectors.

Black Box Functional Testing Techniques 

Here are a few techniques commonly used to perform black box functionality testing.

Equivalence Partitioning

Equivalence partitioning, also known as equivalence class partitioning (ECP), is a black box testing technique that divides the input data of a software unit into partitions of equivalent data. The primary purpose of this technique is to reduce the number of test cases to a manageable size while still ensuring the coverage of the application.

The primary principle behind equivalence partitioning is that the system should treat all the cases in an equivalence class the same. Therefore, if a test case from an equivalence class passes, the other test cases from the same class are expected to pass. This method helps to identify and eliminate redundant test cases, thereby saving time and resources.

Boundary Value Analysis

Boundary value analysis (BVA) is another black box testing technique used in software engineering. It’s built on the premise that errors most often occur at the boundaries of the input domain rather than the center. This technique involves creating test cases for the boundary values of the input domain. BVA is very effective at identifying errors without requiring testing of every possible value. 

Decision Table Testing

Decision table testing is a systematic and organized black box testing technique used to deal with complex systems. This technique is beneficial when the system’s behavior is different for different combinations of inputs. It’s often used when there are multiple inputs that can have different values and can result in different outputs.

A decision table represents inputs and outputs in a structured, tabular form, making it easy to understand. It ensures the coverage of all possible combinations, thus making the test cases more comprehensive and robust.

State Transition Testing

State transition testing is a black box testing technique used to test the behavior of a software application for different input conditions given in a sequence. It’s particularly useful when software behavior changes from one state to another following particular actions.

This technique uses a state transition diagram to represent the different states of a system and the transitions from one state to another. It can help validate a software application’s behavior when it has a sequence of events or needs to maintain a specific order of events.

Use Case Testing

Use case testing is a black box testing technique that uses use cases to identify test cases. A use case is a description of a system’s behavior as it responds to an end-user’s need or request.

This testing technique helps in identifying all possible scenarios for a particular functionality. It ensures that the system can handle and respond to every request correctly and effectively.

Common Black Box Security Testing Techniques 

Here are a few techniques used to carry out black box security testing.

Fuzzing

Fuzzing, also known as fuzz testing, is a technique that involves providing invalid, unexpected, or random data as input to the software. The aim of this technique is to find crash or exploit vulnerabilities in the software.

Fuzzing is a powerful technique because it can help identify coding errors and security loopholes that might not be visible during regular testing phases. It can help in identifying buffer overflow vulnerabilities, memory leaks, and more.

Penetration Testing

Penetration Testing, often referred to as pentesting, is a technique in which a simulated attack is performed on the software to identify vulnerabilities. A penetration test attempts to breach the security of the software, just like a real-world attacker would do, but without causing damage and with the goal of discovering and mitigating security issues.

This technique is highly beneficial as it allows testers to identify how an attacker could gain access to the software and what vulnerabilities they could potentially exploit.

Dynamic Application Security Testing (DAST)

Dynamic application security testing (DAST) is a black box security testing approach that evaluates a software application in its runtime environment. Unlike other testing techniques that focus on examining the codebase, DAST focuses on the live application, aiming to find vulnerabilities that might be exploited during real-world operations.

DAST tests the application from an external vantage point, much like an attacker would. This means the technique does not require access to the underlying source code, making it particularly useful for applications where the source is not readily accessible. The method provides an immediate feedback loop, allowing vulnerabilities like runtime issues, server misconfigurations, and application environment vulnerabilities to be detected and addressed in real-time.

Web Application Testing

As web applications become a critical asset for many organizations, web application testing is growing in importance. It involves testing web applications to find vulnerabilities or issues that could affect the functionality, performance, or security of the application.

Black box web application testing can help identify issues like SQL injection, cross-site scripting (XSS), and other vulnerabilities. It ensures that the web application is secure, user-friendly, and performs well under different scenarios.

Black Box Functional Testing: Pros and Cons 

Let’s review some of the pros and cons of using black box testing methods for functional testing.

Pros

  • Simplicity: Black box testing does not require specific programming knowledge, so it allows virtually anyone to be a tester, including those who may not have a deep understanding of the software’s internal workings. This simplicity also speeds up the testing process, as testers can begin writing test cases as soon as the software’s specifications are complete.
  • User-focused: Black box testing encourages testers to disregard the internal system, and to focus on the system’s functionality as a user would. This naturally aligns the focus of testing with the user experience, encouraging testers to discover and understand issues that users would encounter. By focusing on the user experience rather than the technical aspects, black box testing enables creating test cases that more accurately reflect user behavior.
  • Efficient for large code bases: Because it is not necessary to understand the code that powers the software, testers can start working without having to understand a large and complex code base. Also, black box test cases can typically be executed even if there is a change in the underlying system functionality.

Cons

  • Limited coverage: Since black box testing focuses on the system’s functionality, it can miss errors in the system’s structure or inner workings. For example, black box testing may not effectively detect memory leaks or other issues that occur within the system’s structure.
  • Potential for redundancy: Since testers are not privy to the system’s internal structure, they may unknowingly create multiple test cases that check for the same thing. This redundancy can lead to wasted time and resources.
  • Difficulty in identifying complex issues: Since black box testing focuses on the system’s functionality, it may overlook complex issues that arise from the system’s structure or internal workings. For example, issues related to concurrency or data consistency might not be easily identifiable through black box testing.

Black Box Security Testing: Pros and Cons 

Pros

  • Low chance of false positives: In black box security testing, the tester or testing tool attempts to exploit vulnerabilities from the attacker’s perspective. If an exploit succeeds, there is a high chance that the vulnerability really exists. 
  • Reveals hidden vulnerabilities: Another advantage of black box security testing is that it can reveal hidden vulnerabilities. These are issues that may not be apparent during regular operation but could be exploited by malicious individuals or software. 
  • Identifies configuration and deployment issues: A configuration issue could be as simple as a setting that’s been left at its default value, potentially opening the door for an attack. Alternatively, a deployment issue could be a component that hasn’t been properly installed or configured.

Cons

  • Difficulty in pinpointing root cause: Since black box testers do not have access to the internal workings of the system, they can only identify that a problem exists, not why it exists. This can make it difficult to develop a solution, as the underlying cause of the issue may not be apparent.
  • Potential overhead: Running comprehensive black box tests can be resource-intensive, potentially slowing down the system or even causing it to become unresponsive. However, modern dynamic testing tools can operate without slowing down live systems.
  • Incomplete coverage: Because black box testing doesn’t have access to the system’s internal code, they can’t check every line for potential vulnerabilities. This means that some issues could slip through the cracks and go unnoticed until they’re exploited by an attacker.

When to Choose Black Box Testing in Your QA Strategy

Black-box testing becomes important as soon as an application ceases being a set of features and starts functioning as a product. When users, APIs, and third-party services become part of the equation, code quality becomes a poor indicator of success. 

Even if your application follows good design practices, its behavior may be difficult to predict once live traffic comes through it. Black box testing looks at just that.

When developers want an independent assessment of their application’s behavior, they tend to use black box testing. There is no bias towards any implementation decisions or expectations regarding any particular internal logic. What is important here is the response that is provided. 

This is precisely why black box testing becomes critical for customer-facing systems and microservice architectures. Much of their behavior depends on service interactions, which cannot always be determined by looking at code. Additionally, black box testing is perfectly applicable in the context of an already integrated application and in continuous integration / continuous delivery pipelines.

Black Box Testing Metrics and How to Measure Effectiveness

Evaluating black box testing should be much more focused on the nature of what is being tested, rather than just metrics based on the number of test cases. One clear metric is the coverage that is achieved in terms of user journeys, API calls, and workflows being tested in realistic scenarios. In general, coverage that is relevant to how things are used in reality is much more useful than a high number of superficial checks.

Another very clear sign of black box testing being effective lies in the findings. As long as black box testing consistently brings up problems that teams are already familiar with because of real-life events, the testing is effective. False positives should also be tracked because otherwise, confidence in the testing process will be rapidly diminished. Test findings must be reproducible and obvious; they must be directly related to the functioning of the application. Over time, teams can also evaluate whether black box testing is reducing the number of regressions or helping to prevent other kinds of errors in production.

The goal of black box testing is not the volume of checks but the confidence that the application functions correctly.

How Black Box Testing Supports Security Validation

Black box testing is very similar to actual attacker behavior because they do not have the luxury of looking at the codebase and design documentation either. Attackers interact with running applications and analyze how those applications react under certain input conditions. The black box testing process works in the same way.

The testing process is especially good for finding flaws that cannot be detected through static code analysis. Those include things like improper access control, authentication bypasses, misuse of workflows, and API abuse. All of these flaws would be difficult to detect while reviewing code, but they can be uncovered once actual attack scenarios are carried out.

Black box testing produces observable results. Security professionals can demonstrate vulnerabilities and how exploits work. There is no need for discussion based on assumptions because all observations are factual and can be easily demonstrated again. For advanced AppSec operations, black box testing is an invaluable asset in the testing toolkit.

Challenges Teams Face When Applying Black Box Testing

Another pitfall is the view of black box testing as a one-off practice. Black box tests conducted before release become obsolete quickly due to the constantly changing nature of modern software systems. In order to be relevant and useful, black box testing should run continuously and adjust with the development of an application.

The problem of scoping also arises quite frequently. Black box tests configured in such a way that authentication areas, APIs, and complex flows are left uncovered can create a deceptive feeling of being complete. Another major difficulty related to black box testing is the problem with findings. Unreproducible or vague results will not be taken into account, no matter how serious the issue might be.

Another possible solution to the problem of ineffective black box testing would be giving up the practice altogether. This option is chosen by most teams after some initial difficulties with implementation. However, in most cases, the problem lies not with black box testing itself but its application. With proper adjustment and focus on the behavior of an application, black box tests can prove to be invaluable.

Best Practices for Effective Black Box Testing 

Understand the Requirements

Before you can effectively test a system, you need to have a comprehensive understanding of the system requirements. This includes understanding the system’s functionality, the data it will process, and the security requirements it must meet. Without a full grasp of these requirements, it’s impossible to create effective test cases.

Having a comprehensive understanding of the requirements also helps you identify potential problem areas in the application. This knowledge allows you to focus your testing efforts on areas that are likely to have the most issues, thereby increasing the effectiveness of your testing procedures.

Prioritize Test Cases

Not all test cases are of equal importance. Some areas of the application are more critical than others and, therefore, should be tested first.

Prioritizing test cases also means focusing on the functionality that is most important to the end-user. This ensures that critical functionalities are thoroughly tested and functioning correctly before the product is released.

Prioritizing test cases is also a way to manage time and resources effectively. By focusing on the most important test cases first, you can ensure that the most critical parts of the application are tested in case time or resources run out.

Use Diverse Input Data

One of the strengths of black box testing is its ability to uncover errors and bugs that might not be identified in other forms of testing. This is largely achieved through the use of diverse input data.

Using diverse input data means testing the system with a wide range of input. This includes both valid and invalid input. The aim is to test the system’s behavior and reaction to different kinds of input.

Collaborate Closely with Development Teams

Black box testing is not a one-man task. It requires close collaboration with the development team. Testers and developers need to work together to understand the system requirements, develop effective test cases, and interpret the test results.

Collaborating closely with the development team also helps in getting quick feedback on the test results. This feedback is crucial in making necessary changes and improvements to the system.

Moreover, the development team can provide important insights and information that can help in the testing process. For instance, they can provide information on the most critical areas of the application, which can help in prioritizing test cases.

SAST vs DAST: 5 Key Differences and Why to Use Them Both

Table of Content

  1. What Is SAST (Static Application Security Testing)? 
  2. What Is DAST (Dynamic Application Security Testing)? 
  3. SAST vs. DAST Tools: 5 Key Differences 
  4. Combining SAST and DAST for Comprehensive Security 
  5. Bright Security: The Ultimate Next-Generation DAST Solution

What Is SAST (Static Application Security Testing)? 

SAST, or Static Application Security Testing, is a type of security testing that examines the application’s source code at a static, or non-running, state. This method of testing is often referred to as “white box” testing because it provides a comprehensive view of the application’s code, allowing for a thorough examination of potential vulnerabilities.

SAST is typically performed early in the development lifecycle, often even before the code is executed. The primary aim of SAST is to identify vulnerabilities and flaws in the software’s code that could potentially lead to security breaches. By reviewing the code in its non-running state, SAST can help identify issues like input validation errors, buffer overflows, and insecure server configurations.

While SAST is a powerful tool for identifying potential security issues, it’s not without its challenges. The static nature of SAST means it can’t identify runtime vulnerabilities, and it can sometimes produce false positives. However, when used correctly and in conjunction with other testing methods, SAST can be a valuable part of a comprehensive security strategy.

What Is DAST (Dynamic Application Security Testing)? 

Dynamic Application Security Testing (DAST), on the other hand, is a “black box” testing methodology. This means that unlike SAST, DAST doesn’t require access to the application’s source code. Instead, DAST tests the application in its running state, simulating the actions of an attacker to identify potential vulnerabilities.

DAST is typically performed later in the development cycle, often just before deployment. It aims to identify vulnerabilities that may not be evident in the source code but can become exploitable once the application is running. This includes vulnerabilities like cross-site scripting (XSS), SQL injection, and insecure server configurations.

While DAST offers a valuable perspective on potential runtime vulnerabilities, it also comes with its set of challenges. DAST can sometimes miss vulnerabilities that are not exploitable in the running state, and it can produce false negatives, for example in the case of business logic vulnerabilities. However, many of these shortcomings are overcome by next-generation DAST solutions.

In this article:

SAST vs. DAST Tools: 5 Key Differences 

1. Stage of Implementation

SAST is implemented at the early stages of the software development lifecycle (SDLC). It analyzes source code or binary code for security vulnerabilities, even before the code is compiled and the application is running. This early detection allows for immediate remediation of potential vulnerabilities, saving time and resources.

On the other hand, DAST, also known as “black box testing,” is implemented after the application is running. It tests the application in its operating environment, simulating real-world attacks to identify vulnerabilities. 

While this approach may seem reactive, it provides a realistic view of the application’s security posture, essential for understanding its behavior under attack. In addition, modern DAST tools can be integrated into the software development lifecycle (SDLC), so they can be run during testing stages, long before the application is in production.

2. Nature of Testing

SAST analyzes the source code or binary code. It examines the application from the inside, looking for common coding errors and security loopholes. It’s a proactive approach that aims to prevent security threats from the ground up.

In contrast, DAST examines the application from the outside. It interacts with the application’s exposed interfaces, treating the application as a black box without any knowledge of its internal workings. This approach detects vulnerabilities that may not be apparent during the development process but could be exploited when the application is in its operating environment.

3. Depth vs. Breadth

SAST provides depth—it can identify vulnerabilities deep within the code, which may not become apparent until specific conditions are met. It provides detailed insights into the code, making it a great tool for developers who want to understand and improve their code’s security.

DAST, meanwhile, offers breadth—it tests the application’s entire exposed surface, identifying vulnerabilities that may arise from the interaction between different parts of the application. DAST tools can be used to test thousands of possible attack patterns. While it may not provide the same level of detail as SAST, it provides a comprehensive view of the application’s security, making it invaluable for assessing the application’s overall risk. 

4. Vulnerabilities Detected

SAST is excellent at detecting issues like buffer overflows, SQL injections, and cross-site scripting (XSS) at the code level. It can also identify insecure coding practices that could potentially lead to security vulnerabilities.

While DAST can also detect these types of vulnerabilities by simulating attacks, it excels in identifying runtime vulnerabilities such as server configuration errors, application-level denial of service (DoS) attacks, and other vulnerabilities that result from the application’s interaction with its environment. It’s invaluable for detecting vulnerabilities that aren’t code-related, which SAST may miss.

5. Potential for False Positives and Negatives

No tool is perfect, and both SAST and DAST have their potential for false positives and negatives. False positives—where the tool incorrectly identifies a vulnerability—are common in SAST due to its in-depth code analysis. It can sometimes misinterpret safe code as vulnerable, leading to unnecessary remediation efforts.

DAST, on the other hand, has a higher likelihood of false negatives—where it fails to detect a real vulnerability. Its black-box approach can miss vulnerabilities hidden deep within the application’s code or those that only become apparent under specific conditions. 

However, DAST’s false positives are generally lower than SAST as it tests the application in its running state, providing a more realistic view of potential vulnerabilities. In addition, next-generation DAST solutions use fuzzing and AI technology to reduce false positives and negatives to virtually zero.

Related content: Read our guide to DAST tools

Combining SAST and DAST for Comprehensive Security 

While SAST and DAST have their differences, they are not mutually exclusive. In fact, using them in conjunction provides a more comprehensive view of the application’s security, addressing the limitations of each tool.

Incorporating both SAST and DAST into the SDLC can significantly enhance the security coverage. SAST can be used in the early development stages to identify and rectify potential vulnerabilities at the code level. DAST can then be implemented once the application is running, to detect any runtime vulnerabilities and assess the application’s behavior under attack conditions.

This combination provides a holistic view of the application’s security, ensuring that both code-level and runtime vulnerabilities are identified and mitigated. It allows for a proactive and reactive approach to security, ensuring that all bases are covered.

Related content: Read our guide to dast vs penetration testing.

Bright Security: The Ultimate Next-Generation DAST Solution

Bright Security tests every aspect of your apps. It enables you to scan any target, including web applications, internal applications, APIs (REST/SOAP/GraphQL), websockets, and server side mobile applications. It seamlessly integrates with the tools and workflows you already use, automatically triggering scans on every commit, pull request or build with unit testing. Scans are blazing fast, enabling Bright to work in a high velocity development environment.

Instead of just crawling applications and guessing, Bright interacts intelligently with applications and APIs. Our AI-powered engine understands application architecture and generates sophisticated and targeted attacks. By first verifying and exploiting the findings, we make sure we don’t report any false positives. 

Key features include:

  • Seamlessly integrates with existing tools and workflows—works with your existing CI/CD pipelines. Trigger scans on every commit, pull request or build with unit testing.
  • Spin-up, configure and control scans with code—one file, one command, one scan with no need for UI-based configuration.
  • Super-fast scans—interacts with applications and APIs, instead of just crawling them and guessing. Scans are made faster by an AI-powered engine that can understand application architecture and generate sophisticated and targeted attacks.
  • No false positives—uses AI analysis and fuzz testing to avoid returning false positives, so developers and testers can focus on releasing code.

Get a free plan and try Bright Security today!

Why Running DAST in Production is Not a Good Idea

Table of Content

  1. Risk of Downtime
  2. Data Sensitivity
  3. False Positives and Alert Fatigue
  4. Impact on User Experience
  5. Regulatory and Compliance Issues
  6. Shift Testing Left with Integrated Development Environment (IDE) Integration
  7. Early Detection of Vulnerabilities
  8. Seamless Developer Experience
  9. Real-Time Feedback
  10. Improved Collaboration between Security and Development Teams
  11. Automation and CI/CD Integration
  12. Contextual Understanding
  13. Reduced Risk
  14. Conclusion

Dynamic Application Security Testing (DAST) has long been a cornerstone of application security, helping organizations find and fix vulnerabilities in their applications and APIs. While DAST is typically run early in the software development lifecycle (SDLC), there are some proponents in the industry evangelizing the value of running DAST in production exclusively. Their arguments typically center around DAST scans breaking builds and slowing down the development process. 

However, the practice of running DAST in production environments rather than early in the SDLC presents multiple risks and challenges that can actually hinder your security goals. Here’s why you should think twice before running DAST scans on a live production system.

Risk of Downtime

DAST solutions are designed to find vulnerabilities by simulating attack behaviors. While this is effective for uncovering weaknesses, it can also put a strain on your system resources. Running DAST in a production environment risks causing performance degradation, and in the worst-case scenario, could even bring down the application. System downtime leads to customer dissatisfaction, loss of business, and could tarnish your brand reputation.

Data Sensitivity

DAST tests often include data manipulation to check how an application behaves when faced with unexpected or malicious input. When these tests are conducted in a production environment, they interact with live and often sensitive data. Even if the DAST tool itself is secure, there is still a risk that the test could inadvertently expose or corrupt this sensitive data, which could be a compliance issue.

False Positives and Alert Fatigue

Legacy DAST tools are well-known for not always being precise in their findings to say the least. Running these tools in a production environment will inevitably generate alerts. The notorious problem arises when these alerts include false positives, which need to be triaged and checked manually. This leads to alert fatigue among application security teams, who may then miss genuinely critical alerts amid the noise.

Impact on User Experience

DAST in a production environment can result in degraded performance, leading to a poor user experience. Even short periods of sluggish performance or downtime can result in immediate negative customer feedback, and in today’s digital age, customer experience is paramount. 

Regulatory and Compliance Issues

Regulatory standards like GDPR, HIPAA, and PCI DSS have stringent requirements for how data is handled and secured. Running DAST scans in production could risk non-compliance with these regulations, leading to legal issues and fines.

So what’s the alternative? Here’s a better approach:

Shift Testing Left with Integrated Development Environment (IDE) Integration

Running Dynamic Application Security Testing (DAST) from an Integrated Development Environment (IDE) offers several compelling advantages that can significantly streamline the development process, enhance security, and contribute to more robust, resilient applications. Here’s why it’s a good idea:

Early Detection of Vulnerabilities

The earlier a vulnerability is detected in the Software Development Life Cycle (SDLC), the cheaper and simpler it is to fix. Running DAST from an IDE allows developers to find and address vulnerabilities as they write code, essentially “shifting left” in the SDLC. This early detection helps to ensure that security is integrated into the development process right from the start. Industry research clearly shows that fixing vulnerabilities in production can easily cost ten times more than earlier in the development lifecycle. 

Seamless Developer Experience

For developers, the IDE is their main workspace where they spend most of their time coding, debugging, and testing. Being able to run DAST scans directly from the IDE eliminates the need to switch between different tools, thereby providing a more seamless and efficient user experience. This integration also makes it easier for developers to adopt security testing as a regular part of their workflow.

Real-Time Feedback

Running DAST from an IDE allows for real-time, immediate feedback. As developers write or modify code, they can run quick scans to assess the security impact of their changes. This real-time feedback loop enables developers to understand the security implications of their code as they write it, enhancing both the learning process and the quality of the resulting application.

Improved Collaboration between Security and Development Teams

Embedding DAST within the IDE makes security more accessible for developers, which can foster better collaboration between Application Security (AppSec) and development teams. When developers are equipped with the tools to perform initial security tests themselves, it frees up security teams to focus on more advanced threats and vulnerabilities, making the entire process more efficient.

Automation and CI/CD Integration

When DAST is integrated into an IDE, it can also be easily incorporated into Continuous Integration/Continuous Deployment (CI/CD) pipelines. This enables automated security testing as part of the build process, further ensuring that applications are secure well before they are deployed.

Contextual Understanding

Running DAST scans within an IDE allows developers to see security issues in the context of their code. Unlike running scans on a deployed application where the results may be somewhat abstract, scanning within the IDE allows developers to directly relate the issues to the code they are working on, facilitating quicker and more accurate remediation.

Reduced Risk

By catching vulnerabilities early and incorporating security into the daily workflow of developers, running DAST from an IDE significantly reduces the risk of insecure code making it to production. This not only protects your organization from potential breaches but also from the reputational damage and regulatory fines that can come with security incidents.

Integrating DAST into the IDE creates a more agile, efficient, and secure development process. It allows for early vulnerability detection, encourages a culture of security, and ultimately leads to the creation of more secure applications.

Conclusion

DAST remains a vital tool in any application security toolkit but running these tests in production environments poses more risks than benefits and is not a best practice. By taking a more strategic approach that involves early-stage testing, continuous monitoring, and leveraging alternative testing methods, organizations can maintain the integrity and security of their applications without compromising their production environments. Integrating DAST into the IDE creates a more agile, efficient, and secure development process. It allows for early vulnerability detection, encourages a culture of security, and ultimately leads to the creation of more secure applications.